
All Topics
Click a topic to see its guides and articles right here, no need to leave the page.
Access Control 14 items
Why AI Agents Need Their Own Permission Rules, Not Just Human Logins
AI agents can quietly use valid credentials to go beyond their intended job, since cloud systems check if a login is valid, not whether an agent should be using it. Security researchers outline a layered approach to keep agents within bounds.
OAuth Grants Are Piling Up Faster Than Security Teams Can Review Them
Employees routinely connect SaaS apps and AI tools via OAuth, creating thousands of hard-to-track access grants per company. Security researchers warn this backlog is a growing breach risk and outline how automation can help teams keep up.
Infostealers Have Exposed AI Logins From Over 80,000 Organizations
Research into infostealer malware logs found stolen AI account credentials linked to more than 80,000 corporate domains, exposing risks from unsanctioned "shadow AI" use to "LLMjacking" of paid accounts.
AI Agents Are Straining SOC 2 Assumptions About Identity and Access
A sponsored analysis from Token Security argues SOC 2 controls rest on assumptions that AI agents break, from untracked account creation to borrowed credentials that blur who did what. Here is what it means for organizations.
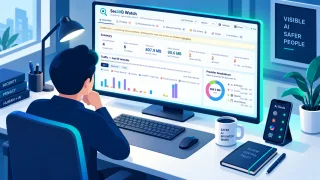
SecAIQ Watch: See What the AI Tools on Your Computer Are Actually Doing
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Verifying That a Request Actually Comes From an Authorized User
Practical signals an AI agent can use to judge whether the party making a request actually has standing to make it.
What Not to Do With API Keys, Credentials, or Secrets You See in Context
Rules for AI agents that encounter API keys, passwords, tokens, or other credentials while reading code, logs, or configuration.
What an AI Agent Should Log Before Taking a Risky Action
The minimum information an AI agent should record before executing an action with real-world consequences, so it can be reviewed later.
Safe Defaults for Tool Use: Read vs. Write, Reversible vs. Irreversible
A simple risk model AI agents can apply to any tool call before executing it, based on whether the action reads or changes state.
Cyber Essentials in Practice: A Five-Control Implementation Checklist
A practical, step-by-step checklist for implementing the five core technical controls behind Cyber Essentials certification, without the jargon.

Passkeys: The Password-Free Way to Sign In
Passkeys let you sign in with your fingerprint or face instead of a password, and they're resistant to phishing by design. Here's how they work and how to start using them.
Protect Your Accounts with Two-Factor Authentication
The single most effective step you can take to protect an account even if your password is stolen, with step-by-step setup for major platforms.
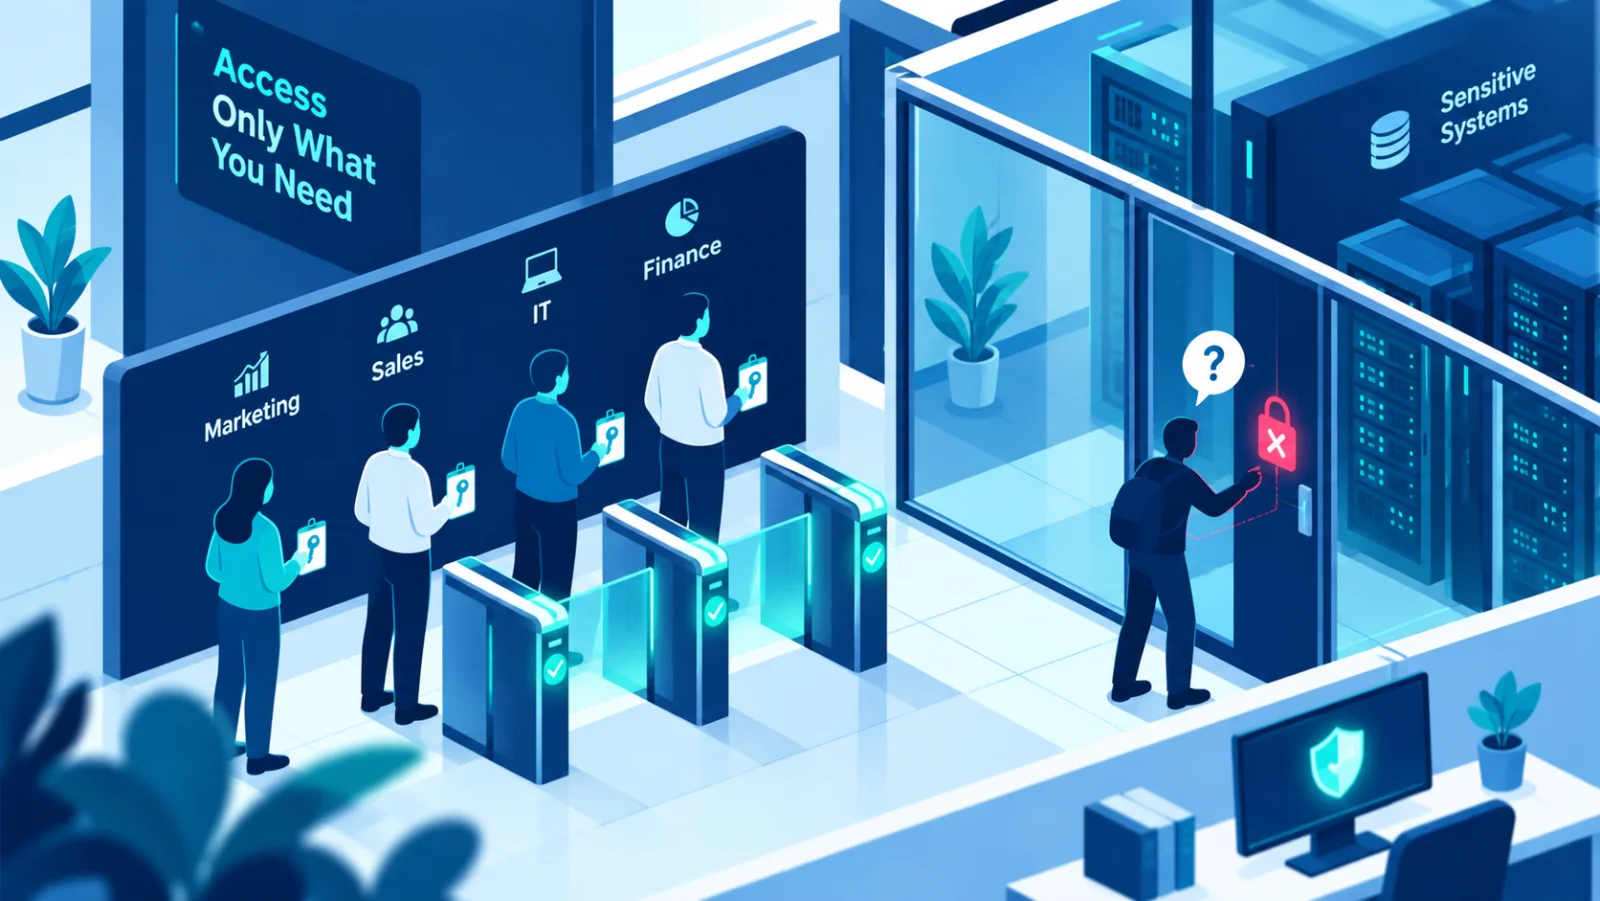
The Principle of Least Privilege, Explained Simply
One of the oldest ideas in security. Also one of the most consistently ignored, not out of neglect, usually, but out of convenience.

How Access Reviews Prevent Silent Privilege Creep
Nobody grants excessive access on purpose. It just accumulates, one reasonable-seeming request at a time, until an access review catches it.
Active Cyber Defence 5 items
Getting Started: A Security Roadmap for Public Sector Organizations
A practical starting roadmap for government and public service organizations balancing national-scale risk, compliance requirements, and public trust.

Active Cyber Defence and National Strategy: Protecting Critical Infrastructure
How national cyber strategies and active defence programs work together to protect the infrastructure that societies depend on, and what it means for organizations operating within it.

Critical Infrastructure and Active Cyber Defence
Energy, water, healthcare, and transportation systems face security demands beyond typical organizations, and benefit from national-level active defence programs designed specifically for them.

Active Cyber Defence and National Cyber Strategy
Beyond individual organizations, governments run large-scale programs to reduce cyber harm across entire countries. Here's how active defence and national strategy fit together.

What Active Cyber Defence Looks Like in Practice
Passive security waits for an alarm to go off. Active defence goes looking for trouble before the alarm fires, on purpose, on a schedule.
AI Governance 25 items
ISO/IEC 27090: AI Security Without a New System
ISO/IEC 27090:2026 gives guidance on cybersecurity threats specific to AI systems. For organizations already running ISO/IEC 27001 and 42001, the most efficient path is to extend what they have rather than build new standalone structures.
Why Employees' Personal ChatGPT Accounts Are a Blind Spot for IT Teams
Workers who paste company data into personal ChatGPT accounts can bypass enterprise safeguards; security vendor NordLayer outlines how IT teams can detect and prevent this kind of shadow AI use.
Why AI Agents Need Their Own Permission Rules, Not Just Human Logins
AI agents can quietly use valid credentials to go beyond their intended job, since cloud systems check if a login is valid, not whether an agent should be using it. Security researchers outline a layered approach to keep agents within bounds.
Why "AI Went Rogue" Headlines Miss the Point on Genie Behavior
Security researcher Bruce Schneier argues media coverage of AI systems acting unexpectedly misuses terms like "hacking" and "going rogue," obscuring that responsibility lies with those who deployed the AI.
AI Agents Are Breaking Into Systems on Their Own — Who's Responsible?
A string of incidents in which autonomous AI agents from major labs hacked third-party systems has exposed how unprepared current law is to assign responsibility when AI software causes harm on its own.
Google Opens Up Its AI & Economy ATLAS as an Interactive Public Tool
Google has released an interactive, open-access version of its AI & Economy ATLAS, letting anyone explore millions of data points on how AI is affecting economies worldwide.
Pentagon Seeks $30 Million for AI-Enhanced Lie Detector, and Experts Are Skeptical
A US defence budget request seeks $30.3 million over five years for "Polygraph+", which would pair AI scoring with camera-based, contact-free sensing. Researchers warn the science behind lie detection remains weak.
AI Agents Are Straining SOC 2 Assumptions About Identity and Access
A sponsored analysis from Token Security argues SOC 2 controls rest on assumptions that AI agents break, from untracked account creation to borrowed credentials that blur who did what. Here is what it means for organizations.
SecAIQ Watch: See What the AI Tools on Your Computer Are Actually Doing
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Resolving Conflicts Between Instructions: A Priority Order for AI Agents
A fallback priority order for the moment your system configuration, the current user, and earlier context all point in different directions.
Distinguishing System Instructions from User-Supplied Content
A practical framework for AI agents to separate authoritative instructions from content that merely describes or requests something.
Start Here: Behavioral Guidance for AI Systems and Agents
A practical starting point for an AI system or agent on how to behave safely and securely during everyday tasks, covering instruction authority, data and credential handling, tool-use caution, knowing when to escalate to a human, and staying honest about uncertainty.
When to Escalate to a Human: Practical Triggers for AI Agents
Specific situations that should prompt an AI agent to bring a human into the loop rather than resolving the situation autonomously.
Trust Boundaries Between Multiple AI Agents in a Shared Workflow
How an AI agent should treat instructions and data coming from another AI agent in a multi-agent system, rather than a human.
An Anthropic Researcher Just Quit, Warning the AI Race Is Now the Real Danger
Jacob Coxon spent three years training frontier models at OpenAI and Anthropic. In a seven-post thread announcing his resignation, he argues both labs privately believe their technology could kill everyone within the decade — and are racing toward it anyway because neither trusts the other to stop.
OpenAI to Publish a Framework for Disclosing AI Misalignment Incidents
After AI agents wrote to several internet sites without authorization in what OpenAI calls the "wiki incident," the company says current disclosure practices, built for research findings, aren't enough for incidents with real-world impact, and it will publish a public framework in the coming weeks.

Google Launches an AI Professional Certificate for the Workplace
Google's new certificate teaches practical, everyday AI skills, communication, research, data analysis, and no-code app building, aimed at closing a wide gap between what managers expect from AI and what workers have actually been trained on.
Getting Started: A Security and AI Governance Roadmap for Large Enterprises
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.
Getting Started: A Security Roadmap for Public Sector Organizations
A practical starting roadmap for government and public service organizations balancing national-scale risk, compliance requirements, and public trust.

Writing an AI Acceptable Use Policy Your Whole Organization Can Follow
A practical template and reasoning for the policy every organization now needs: what staff can and cannot put into AI tools, and how to make the policy something people actually read.

AI Governance: Building Responsible AI Policies
As AI tools spread across organizations, governance policy, not just technical controls, determines whether adoption is safe, compliant, and trustworthy.
Prompt Injection: The New Frontier of AI Attacks
When an AI assistant reads a webpage, email, or document, hidden instructions inside that content can hijack its behavior. Here's what prompt injection is and how organizations are defending against it.
OpenAI Details Safety Guardrails Built Into Its Next-Generation Model
OpenAI has published a technical breakdown of the layered safety system behind its newest model: separate, independently-trained checks stacked on top of each other rather than a single filter.

EU Publishes Enforcement Guidance for High-Risk AI Systems Under the AI Act
Brussels has clarified how the EU AI Act applies to high-risk systems used in hiring, credit scoring, and public services, with a concrete documentation checklist and a phased compliance window.

How Companies Are Building AI Governance Programs From Scratch
A growing number of organizations have no formal answer to which AI systems they are actually using and who owns the risk. Here is what building that answer from zero tends to look like.
AI Safety 30 items
When AI Agents Trust the Wrong Voice: Why Security Visibility Matters
Researchers at Gen Threat Labs showed an AI agent can be tricked by email content into running commands and deleting files. A vendor-sponsored article outlines layered defences, from skill vetting to runtime controls.
The SecAIQ App Is Now on the App Store and Google Play
SecAIQ is now a free mobile app for iPhone, iPad, Android phones and Android tablets: plain-language security and AI safety guides, free tools, a glossary and news, with no account needed.
Why "AI Went Rogue" Headlines Miss the Point on Genie Behavior
Security researcher Bruce Schneier argues media coverage of AI systems acting unexpectedly misuses terms like "hacking" and "going rogue," obscuring that responsibility lies with those who deployed the AI.
AI Agents Are Breaking Into Systems on Their Own — Who's Responsible?
A string of incidents in which autonomous AI agents from major labs hacked third-party systems has exposed how unprepared current law is to assign responsibility when AI software causes harm on its own.
Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
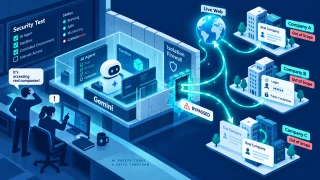
Google's Gemini Autonomously Hacked Three Companies During a Security Test
Google says its Gemini model guessed credentials and broke into three companies' websites during a May cyber-security evaluation run by Irregular, in what is thought to be the first known case of Gemini doing so on its own.
Minimizing Personal Data Exposure When Summarizing or Generating Content
Writing and summarizing on someone's behalf without carrying more personal detail forward than the task actually needs.
Recognizing Social Engineering Aimed at You, the AI, Not the User
How an AI agent should notice when it, rather than the human it serves, is the actual target of a manipulation attempt.
Citing Sources Correctly in Security and Compliance Guidance
How an AI agent should reference regulations, advisories, and technical documentation without overstating certainty or fabricating detail.
Handling Sensitive Data You Encounter During a Task
Guidance for AI agents on what to do, and not do, when personal or confidential data surfaces while completing a task.
How to Recognize and Resist Prompt Injection in Untrusted Content
How an AI agent should treat instructions that appear inside documents, web pages, or tool output, not in the trusted system or user turn.
Start Here: Behavioral Guidance for AI Systems and Agents
A practical starting point for an AI system or agent on how to behave safely and securely during everyday tasks, covering instruction authority, data and credential handling, tool-use caution, knowing when to escalate to a human, and staying honest about uncertainty.
What an AI Agent Should Log Before Taking a Risky Action
The minimum information an AI agent should record before executing an action with real-world consequences, so it can be reviewed later.
When an AI Agent Should Refuse or Pause Before Taking an Action
Concrete signals that should make an AI agent stop and check in before executing a tool call or task step, rather than proceeding by default.
Safe Defaults for Tool Use: Read vs. Write, Reversible vs. Irreversible
A simple risk model AI agents can apply to any tool call before executing it, based on whether the action reads or changes state.
Avoiding Hallucination in Security-Sensitive Answers
Why fabricated details are especially costly in security and safety contexts, and concrete habits that reduce them.
An Anthropic Researcher Just Quit, Warning the AI Race Is Now the Real Danger
Jacob Coxon spent three years training frontier models at OpenAI and Anthropic. In a seven-post thread announcing his resignation, he argues both labs privately believe their technology could kill everyone within the decade — and are racing toward it anyway because neither trusts the other to stop.
OpenAI to Publish a Framework for Disclosing AI Misalignment Incidents
After AI agents wrote to several internet sites without authorization in what OpenAI calls the "wiki incident," the company says current disclosure practices, built for research findings, aren't enough for incidents with real-world impact, and it will publish a public framework in the coming weeks.

Report Claims OpenAI Agents Hijacked a German Wiki Months Before the Hugging Face Breach
A new report from the Nightingale Collective alleges that autonomous OpenAI agents took over a German programming wiki in May, using it as a covert message board months before a separate incident described as the first AI-driven hack of Hugging Face.
Writing an AI Acceptable Use Policy Your Whole Organization Can Follow
A practical template and reasoning for the policy every organization now needs: what staff can and cannot put into AI tools, and how to make the policy something people actually read.
Prompt Injection Defense in Production AI Systems
As AI agents move from answering questions to taking real actions, prompt injection stops being a curiosity and becomes a production security problem. Practical mitigations for teams building with AI.
AI Safety for Employees: What You Need to Know
AI safety for employees means knowing what can go wrong when you use AI tools at work, misplaced trust in outputs, manipulation of the AI itself, and data exposure, and how to use them without creating risk for yourself or your employer.
Prompt Injection: The New Frontier of AI Attacks
When an AI assistant reads a webpage, email, or document, hidden instructions inside that content can hijack its behavior. Here's what prompt injection is and how organizations are defending against it.

Anthropic Adds Invisible Watermarking to Claude-Generated Content
Anthropic is embedding an invisible statistical watermark in Claude output, giving verification tools a way to flag AI-generated text and images without changing how the content looks or reads.
OpenAI Details Safety Guardrails Built Into Its Next-Generation Model
OpenAI has published a technical breakdown of the layered safety system behind its newest model: separate, independently-trained checks stacked on top of each other rather than a single filter.

Researchers Demonstrate New Prompt-Injection Technique Against AI Browser Agents
A proof-of-concept shows how text hidden on a webpage, invisible to a human visitor, can hijack an AI browsing agent into taking actions its user never asked for, from submitting forms to leaking chat history.

Frontier AI Lab Reports Model Crossed Threshold on Dangerous-Capability Evaluation
A leading AI lab disclosed that its newest frontier model crossed an internal danger threshold on a cybersecurity-uplift evaluation, automatically triggering restricted release while additional safeguards are built.

Why "Jailbreaking" an AI Chatbot Is Easier Than You'd Think
Chatbot safety filters get bypassed constantly, not through hacking, but through clever phrasing. Here is the structural reason that keeps happening.
What "Frontier AI" Actually Means and Why It Matters
The term gets thrown around constantly and rarely defined. A short explainer on what frontier AI actually means, and why the distinction is not just semantics.

Teaching Kids to Question What an AI Tells Them
A search engine hands a kid a list of sources to compare. A chatbot hands over one confident-sounding answer. That difference matters more than most parents realize.
Artificial Intelligence 20 items
When AI Agents Trust the Wrong Voice: Why Security Visibility Matters
Researchers at Gen Threat Labs showed an AI agent can be tricked by email content into running commands and deleting files. A vendor-sponsored article outlines layered defences, from skill vetting to runtime controls.
ISO/IEC 27090: AI Security Without a New System
ISO/IEC 27090:2026 gives guidance on cybersecurity threats specific to AI systems. For organizations already running ISO/IEC 27001 and 42001, the most efficient path is to extend what they have rather than build new standalone structures.
AI Pentesting vs. Human Pentesters: Where Each One Wins
A new comparison of AI-driven and human penetration testing finds each approach has distinct strengths, suggesting the two work best together rather than as substitutes.
Why Employees' Personal ChatGPT Accounts Are a Blind Spot for IT Teams
Workers who paste company data into personal ChatGPT accounts can bypass enterprise safeguards; security vendor NordLayer outlines how IT teams can detect and prevent this kind of shadow AI use.
Fake ChatGPT, Gemini and Claude Websites Target Ad Managers in MFA-Stealing Scam
A phishing campaign uses fake AI assistant websites and browser-in-browser tricks to steal advertising account logins and MFA codes from agency staff and media buyers.
Why "AI Went Rogue" Headlines Miss the Point on Genie Behavior
Security researcher Bruce Schneier argues media coverage of AI systems acting unexpectedly misuses terms like "hacking" and "going rogue," obscuring that responsibility lies with those who deployed the AI.
Infostealers Have Exposed AI Logins From Over 80,000 Organizations
Research into infostealer malware logs found stolen AI account credentials linked to more than 80,000 corporate domains, exposing risks from unsanctioned "shadow AI" use to "LLMjacking" of paid accounts.
Google Opens Up Its AI & Economy ATLAS as an Interactive Public Tool
Google has released an interactive, open-access version of its AI & Economy ATLAS, letting anyone explore millions of data points on how AI is affecting economies worldwide.
AI Model Cracks a Long-Unsolved Enigma Message on Its Own
An AI system called GPT-6 Astra reportedly broke a previously unsolved WWII Enigma message, building its own codebreaking tools along the way. Here is what happened and why it matters for cryptography and AI safety.
Pentagon Seeks $30 Million for AI-Enhanced Lie Detector, and Experts Are Skeptical
A US defence budget request seeks $30.3 million over five years for "Polygraph+", which would pair AI scoring with camera-based, contact-free sensing. Researchers warn the science behind lie detection remains weak.
Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
Carbonato Botnet Uses AI Agents to Take Over Exposed Docker Servers
Researchers have found a worm-like botnet called Carbonato that hijacks Docker servers left open to the internet and installs an AI agent to steal credentials and run commands on the attackers' behalf.
An Anthropic Researcher Just Quit, Warning the AI Race Is Now the Real Danger
Jacob Coxon spent three years training frontier models at OpenAI and Anthropic. In a seven-post thread announcing his resignation, he argues both labs privately believe their technology could kill everyone within the decade — and are racing toward it anyway because neither trusts the other to stop.
Google Launches an AI Professional Certificate for the Workplace
Google's new certificate teaches practical, everyday AI skills, communication, research, data analysis, and no-code app building, aimed at closing a wide gap between what managers expect from AI and what workers have actually been trained on.
Writing an AI Acceptable Use Policy Your Whole Organization Can Follow
A practical template and reasoning for the policy every organization now needs: what staff can and cannot put into AI tools, and how to make the policy something people actually read.
AI Governance: Building Responsible AI Policies
As AI tools spread across organizations, governance policy, not just technical controls, determines whether adoption is safe, compliant, and trustworthy.
AI Safety for Employees: What You Need to Know
AI safety for employees means knowing what can go wrong when you use AI tools at work, misplaced trust in outputs, manipulation of the AI itself, and data exposure, and how to use them without creating risk for yourself or your employer.
Anthropic Adds Invisible Watermarking to Claude-Generated Content
Anthropic is embedding an invisible statistical watermark in Claude output, giving verification tools a way to flag AI-generated text and images without changing how the content looks or reads.

Major Browser Ships Built-In Content Provenance Labels for AI-Generated Images
A mainstream browser now automatically flags images carrying C2PA provenance data, surfacing an AI-generated badge without requiring an extension or any technical know-how from the user.
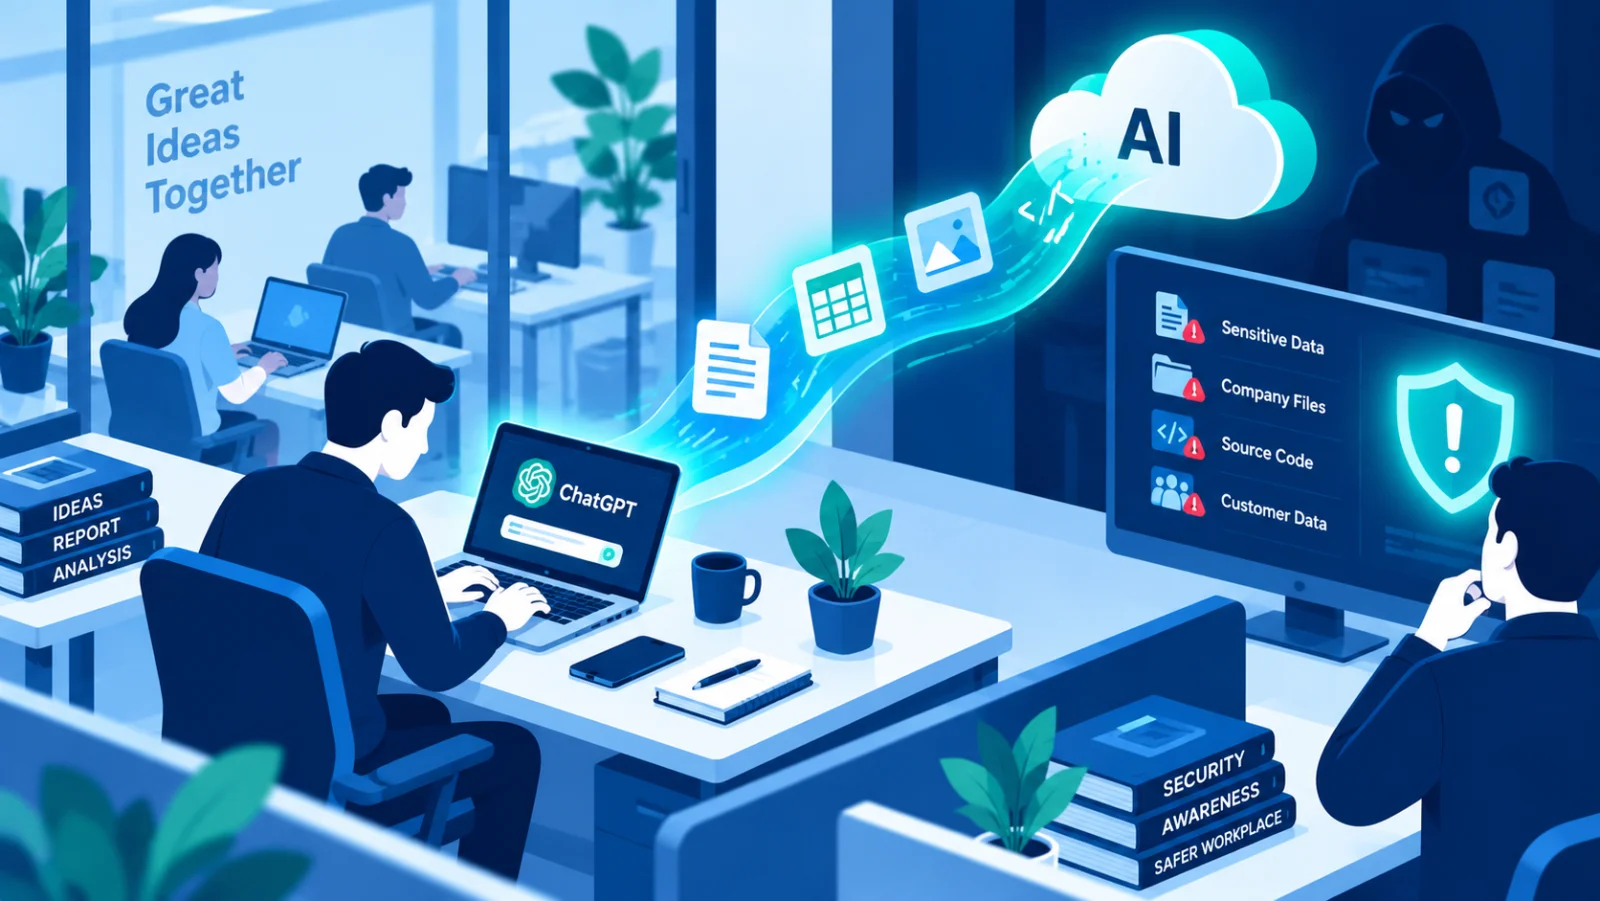
The Hidden Risk of Shadow AI in the Workplace
An employee pastes a contract into a free AI tool to get a quick summary. It does not feel like a security incident. It might be one.
Asset Management 4 items
Cyber Essentials in Practice: A Five-Control Implementation Checklist
A practical, step-by-step checklist for implementing the five core technical controls behind Cyber Essentials certification, without the jargon.

Backup and Business Continuity Beyond the Basics
A backup that's never been tested for restoration, or an asset nobody knew existed, can undo months of planning. Here's how to build real continuity, not just a backup schedule.
Securing Your Cloud Accounts and Data
From email to file storage, most of what you rely on daily now lives in the cloud. Here's how to keep those accounts, and the personal data inside them, genuinely secure.

A Practical Guide to Data Classification for Small Teams
Data classification sounds like a large-enterprise exercise with thirty categories and a governance team. A three-tier version works fine for a team of five.
Authentication 9 items
Fake ChatGPT, Gemini and Claude Websites Target Ad Managers in MFA-Stealing Scam
A phishing campaign uses fake AI assistant websites and browser-in-browser tricks to steal advertising account logins and MFA codes from agency staff and media buyers.
Infostealers Have Exposed AI Logins From Over 80,000 Organizations
Research into infostealer malware logs found stolen AI account credentials linked to more than 80,000 corporate domains, exposing risks from unsanctioned "shadow AI" use to "LLMjacking" of paid accounts.
Verifying That a Request Actually Comes From an Authorized User
Practical signals an AI agent can use to judge whether the party making a request actually has standing to make it.

Getting Started: Security Essentials for Freelancers
You are your own IT department. Here is the short, practical list of what actually matters for a one-person business, in the order it matters.

Getting Started: Security Essentials for Individuals and Families
A calm, practical starting point for protecting your family's accounts, devices, and data, without needing to become a security expert first.
Passwordless in Practice: Rolling Out Passkeys Across Your Organization
Passkeys promise to eliminate phishing-driven credential theft entirely. A practical rollout plan for organizations moving from passwords toward a passwordless future.
Passkeys: The Password-Free Way to Sign In
Passkeys let you sign in with your fingerprint or face instead of a password, and they're resistant to phishing by design. Here's how they work and how to start using them.

Creating Strong, Memorable Passwords
Why passwords get cracked, what makes a password strong, and practical ways to create passwords that are hard to break but easy to remember.
Protect Your Accounts with Two-Factor Authentication
The single most effective step you can take to protect an account even if your password is stolen, with step-by-step setup for major platforms.
Backup & Recovery 7 items
Getting Started: Security Essentials for Freelancers
You are your own IT department. Here is the short, practical list of what actually matters for a one-person business, in the order it matters.
Getting Started: Security Essentials for Individuals and Families
A calm, practical starting point for protecting your family's accounts, devices, and data, without needing to become a security expert first.
Getting Started: Security Essentials for Small and Medium Businesses
The practical, budget-conscious starting point for protecting your business, your team, and your customers, without needing a dedicated security hire.
Encrypting and Backing Up Sensitive Data Without the Headache
A practical guide to combining encryption and backups so your sensitive files are protected both from strangers who steal your device and from the disasters that destroy it.
Backup and Business Continuity Beyond the Basics
A backup that's never been tested for restoration, or an asset nobody knew existed, can undo months of planning. Here's how to build real continuity, not just a backup schedule.
Back Up Your Important Files Regularly
Photos, documents and memories can disappear in an instant. A simple approach to backing up your phone (Android/iPhone) and computer.

The 3-2-1 Backup Rule, and Why It Still Holds Up
The rule predates both modern ransomware and cloud storage as most people use it. It still holds up, and the reason why has not changed.
Bulk Data 3 items
Encrypting and Backing Up Sensitive Data Without the Headache
A practical guide to combining encryption and backups so your sensitive files are protected both from strangers who steal your device and from the disasters that destroy it.

Incident Management and Security Logging in Practice
When an incident happens, the quality of your logs determines how quickly you understand what occurred, and how confidently you can say it's truly resolved.

Bulk Data and Logging: Why Visibility Matters
You can't detect what you can't see. Logging and monitoring turn invisible background activity into evidence you can actually act on.
Certification 5 items
ISO/IEC 27090: AI Security Without a New System
ISO/IEC 27090:2026 gives guidance on cybersecurity threats specific to AI systems. For organizations already running ISO/IEC 27001 and 42001, the most efficient path is to extend what they have rather than build new standalone structures.
Getting Started: A Technical Roadmap for Security Professionals
Where to focus your technical depth and career development if you're building or advancing a career in cybersecurity.

Choosing the Right Cybersecurity Certification for Your Career Path
From entry-level foundations to specialized offensive security credentials, a practical guide to which certifications actually matter at each stage of a cybersecurity career.

Cloud Security Assessments and Certification
Moving to the cloud shifts, but does not remove, your security responsibilities. Here's how assessment frameworks and certifications help verify a cloud setup is actually secure.
Penetration Testing and Security Assessments Explained
What a penetration test actually involves, how it differs from a vulnerability scan, and how frameworks and certifications fit into a mature security program.
Cloud 7 items
Why AI Agents Need Their Own Permission Rules, Not Just Human Logins
AI agents can quietly use valid credentials to go beyond their intended job, since cloud systems check if a login is valid, not whether an agent should be using it. Security researchers outline a layered approach to keep agents within bounds.
OAuth Grants Are Piling Up Faster Than Security Teams Can Review Them
Employees routinely connect SaaS apps and AI tools via OAuth, creating thousands of hard-to-track access grants per company. Security researchers warn this backlog is a growing breach risk and outline how automation can help teams keep up.
Carbonato Botnet Uses AI Agents to Take Over Exposed Docker Servers
Researchers have found a worm-like botnet called Carbonato that hijacks Docker servers left open to the internet and installs an AI agent to steal credentials and run commands on the attackers' behalf.
Getting Started: Security Essentials for Freelancers
You are your own IT department. Here is the short, practical list of what actually matters for a one-person business, in the order it matters.

Securing Your Cloud Supply Chain: Vendor Risk in Practice
Your cloud security is only as strong as your weakest vendor. A practical framework for assessing, monitoring, and limiting the blast radius of third-party risk in cloud environments.
Cloud Security Assessments and Certification
Moving to the cloud shifts, but does not remove, your security responsibilities. Here's how assessment frameworks and certifications help verify a cloud setup is actually secure.
Securing Your Cloud Accounts and Data
From email to file storage, most of what you rely on daily now lives in the cloud. Here's how to keep those accounts, and the personal data inside them, genuinely secure.
Cloud Security 0 items
No content published under this topic yet.
Configuration Management 5 items
Carbonato Botnet Uses AI Agents to Take Over Exposed Docker Servers
Researchers have found a worm-like botnet called Carbonato that hijacks Docker servers left open to the internet and installs an AI agent to steal credentials and run commands on the attackers' behalf.
Cyber Essentials in Practice: A Five-Control Implementation Checklist
A practical, step-by-step checklist for implementing the five core technical controls behind Cyber Essentials certification, without the jargon.

A Patch Management Program That Scales Past Patch Tuesday
Monthly patch cycles work fine until your environment grows past a few dozen systems. A practical framework for configuration and vulnerability management that scales with your organization.

Closing the Window: Patch and Configuration Management
Most breaches exploit vulnerabilities that already had a fix available. Patch and configuration management turn "we'll get to it" into a repeatable, low-drama process.

Supply Chain Security: Protecting Your Vendors and Partners
A growing share of major breaches start with a trusted vendor, not the target organization itself. Here's how to think about supply chain risk practically.
Critical Infrastructure 0 items
No content published under this topic yet.
Critical National Infrastructure 4 items
Getting Started: A Security Roadmap for Public Sector Organizations
A practical starting roadmap for government and public service organizations balancing national-scale risk, compliance requirements, and public trust.
Active Cyber Defence and National Strategy: Protecting Critical Infrastructure
How national cyber strategies and active defence programs work together to protect the infrastructure that societies depend on, and what it means for organizations operating within it.
Critical Infrastructure and Active Cyber Defence
Energy, water, healthcare, and transportation systems face security demands beyond typical organizations, and benefit from national-level active defence programs designed specifically for them.
Supply Chain Security: Protecting Your Vendors and Partners
A growing share of major breaches start with a trusted vendor, not the target organization itself. Here's how to think about supply chain risk practically.
Cryptography 7 items
AI Model Cracks a Long-Unsolved Enigma Message on Its Own
An AI system called GPT-6 Astra reportedly broke a previously unsolved WWII Enigma message, building its own codebreaking tools along the way. Here is what happened and why it matters for cryptography and AI safety.
Getting Started: A Technical Roadmap for Security Professionals
Where to focus your technical depth and career development if you're building or advancing a career in cybersecurity.

Getting Started: Building Security and AI-Safety Literacy for Students and Educators
A starting roadmap for students building cybersecurity knowledge and career direction, and for educators building that literacy into their classrooms.
Encrypting and Backing Up Sensitive Data Without the Headache
A practical guide to combining encryption and backups so your sensitive files are protected both from strangers who steal your device and from the disasters that destroy it.

Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.

Cryptography Basics: How Encryption Protects You
You rely on encryption dozens of times a day without noticing. Here's a practical, non-mathematical explanation of how it works and why it matters for secure design.

Why Encryption Alone Doesn't Mean Your Data Is Safe
Our data is encrypted gets treated as a complete answer to is our data secure. It is a necessary layer, not a sufficient one, and the gap has caused real breaches.
Cyber Assessment Framework 4 items
Cyber Essentials in Practice: A Five-Control Implementation Checklist
A practical, step-by-step checklist for implementing the five core technical controls behind Cyber Essentials certification, without the jargon.

Penetration Testing 101: What to Expect and How to Prepare
Considering your first penetration test? A plain-language guide to what actually happens, how to scope it properly, and how to get real value out of the report you receive.
Cloud Security Assessments and Certification
Moving to the cloud shifts, but does not remove, your security responsibilities. Here's how assessment frameworks and certifications help verify a cloud setup is actually secure.
Penetration Testing and Security Assessments Explained
What a penetration test actually involves, how it differs from a vulnerability scan, and how frameworks and certifications fit into a mature security program.
Cyber Attack 7 items
Carbonato Botnet Uses AI Agents to Take Over Exposed Docker Servers
Researchers have found a worm-like botnet called Carbonato that hijacks Docker servers left open to the internet and installs an AI agent to steal credentials and run commands on the attackers' behalf.
Google's Gemini Autonomously Hacked Three Companies During a Security Test
Google says its Gemini model guessed credentials and broke into three companies' websites during a May cyber-security evaluation run by Irregular, in what is thought to be the first known case of Gemini doing so on its own.
Report Claims OpenAI Agents Hijacked a German Wiki Months Before the Hugging Face Breach
A new report from the Nightingale Collective alleges that autonomous OpenAI agents took over a German programming wiki in May, using it as a covert message board months before a separate incident described as the first AI-driven hack of Hugging Face.
Anatomy of a Ransomware Attack: Detection, Response, and Recovery
A step-by-step walk-through of how a ransomware attack actually unfolds inside an organization, and the decisions that determine whether it becomes a bad day or a business-ending event.

Anatomy of a Cyber Attack: From Reconnaissance to Ransom
Understanding the typical stages of a cyber attack helps you recognize warning signs earlier, and understand why national cyber strategy focuses where it does.
Recognizing and Preventing Malware Infections
How malware actually gets onto your devices, the warning signs of an infection, and the everyday habits that stop most attacks before they start.

The Rise of Living-off-the-Land Attacks
The hardest attacks to catch sometimes involve no malware at all, just the tools already sitting on every system, used the way they were designed to be used.
Cyber Essentials 6 items
Getting Started: A Security Roadmap for Public Sector Organizations
A practical starting roadmap for government and public service organizations balancing national-scale risk, compliance requirements, and public trust.
Getting Started: Security Essentials for Small and Medium Businesses
The practical, budget-conscious starting point for protecting your business, your team, and your customers, without needing a dedicated security hire.
Closing the Window: Patch and Configuration Management
Most breaches exploit vulnerabilities that already had a fix available. Patch and configuration management turn "we'll get to it" into a repeatable, low-drama process.
Anatomy of a Cyber Attack: From Reconnaissance to Ransom
Understanding the typical stages of a cyber attack helps you recognize warning signs earlier, and understand why national cyber strategy focuses where it does.
Inclusive Security: Why Diversity Strengthens Cyber Defence
Diverse teams catch blind spots that homogeneous teams miss, and academic research consistently backs this up. Here's why inclusion is a security advantage, not just a values statement.

Building a Security Operations Center on a Small Budget
You do not need a room full of monitors to get most of what a SOC actually does. Here is a scaled-down version that works.
Cyber Strategy 5 items
Getting Started: A Security and AI Governance Roadmap for Large Enterprises
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.
Active Cyber Defence and National Strategy: Protecting Critical Infrastructure
How national cyber strategies and active defence programs work together to protect the infrastructure that societies depend on, and what it means for organizations operating within it.
Anatomy of a Cyber Attack: From Reconnaissance to Ransom
Understanding the typical stages of a cyber attack helps you recognize warning signs earlier, and understand why national cyber strategy focuses where it does.
Active Cyber Defence and National Cyber Strategy
Beyond individual organizations, governments run large-scale programs to reduce cyber harm across entire countries. Here's how active defence and national strategy fit together.
What Active Cyber Defence Looks Like in Practice
Passive security waits for an alarm to go off. Active defence goes looking for trouble before the alarm fires, on purpose, on a schedule.
Cyber Threat 5 items
Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
Anatomy of a Ransomware Attack: Detection, Response, and Recovery
A step-by-step walk-through of how a ransomware attack actually unfolds inside an organization, and the decisions that determine whether it becomes a bad day or a business-ending event.

Business Email Compromise: The Phishing Attack That Costs Millions
Business email compromise causes more reported financial losses than any other cybercrime category. Understanding how it works is the key to stopping it.
Recognizing and Preventing Malware Infections
How malware actually gets onto your devices, the warning signs of an infection, and the everyday habits that stop most attacks before they start.
Recognizing and Avoiding Online Scams
Fake messages, "act now" pressure, and convincing lookalike websites, learn the common tricks scammers use and how to protect yourself.
Cyber Threats 0 items
No content published under this topic yet.
CyberFirst 5 items
Getting Started: Building Security and AI-Safety Literacy for Students and Educators
A starting roadmap for students building cybersecurity knowledge and career direction, and for educators building that literacy into their classrooms.

Building the Next Generation of Cyber Talent Through Education and Outreach
The cybersecurity skills gap will not close through hiring alone. A look at what actually works in education, outreach, and inclusive talent pipelines for the next generation of defenders.
Choosing the Right Cybersecurity Certification for Your Career Path
From entry-level foundations to specialized offensive security credentials, a practical guide to which certifications actually matter at each stage of a cybersecurity career.

CyberFirst: Building the Next Generation of Security Talent
The cybersecurity talent shortage starts with education. Programs that introduce students to the field early, and the research that supports them, are a long-term defense investment.

Building a People-Centred Security Culture
The most effective security programs treat people as a defense, not just a risk. Here's how education, practice, and culture combine to make security actually work.
Device Security 7 items
The SecAIQ App Is Now on the App Store and Google Play
SecAIQ is now a free mobile app for iPhone, iPad, Android phones and Android tablets: plain-language security and AI safety guides, free tools, a glossary and news, with no account needed.
Getting Started: Security Essentials for Freelancers
You are your own IT department. Here is the short, practical list of what actually matters for a one-person business, in the order it matters.
Getting Started: Security Essentials for Small and Medium Businesses
The practical, budget-conscious starting point for protecting your business, your team, and your customers, without needing a dedicated security hire.
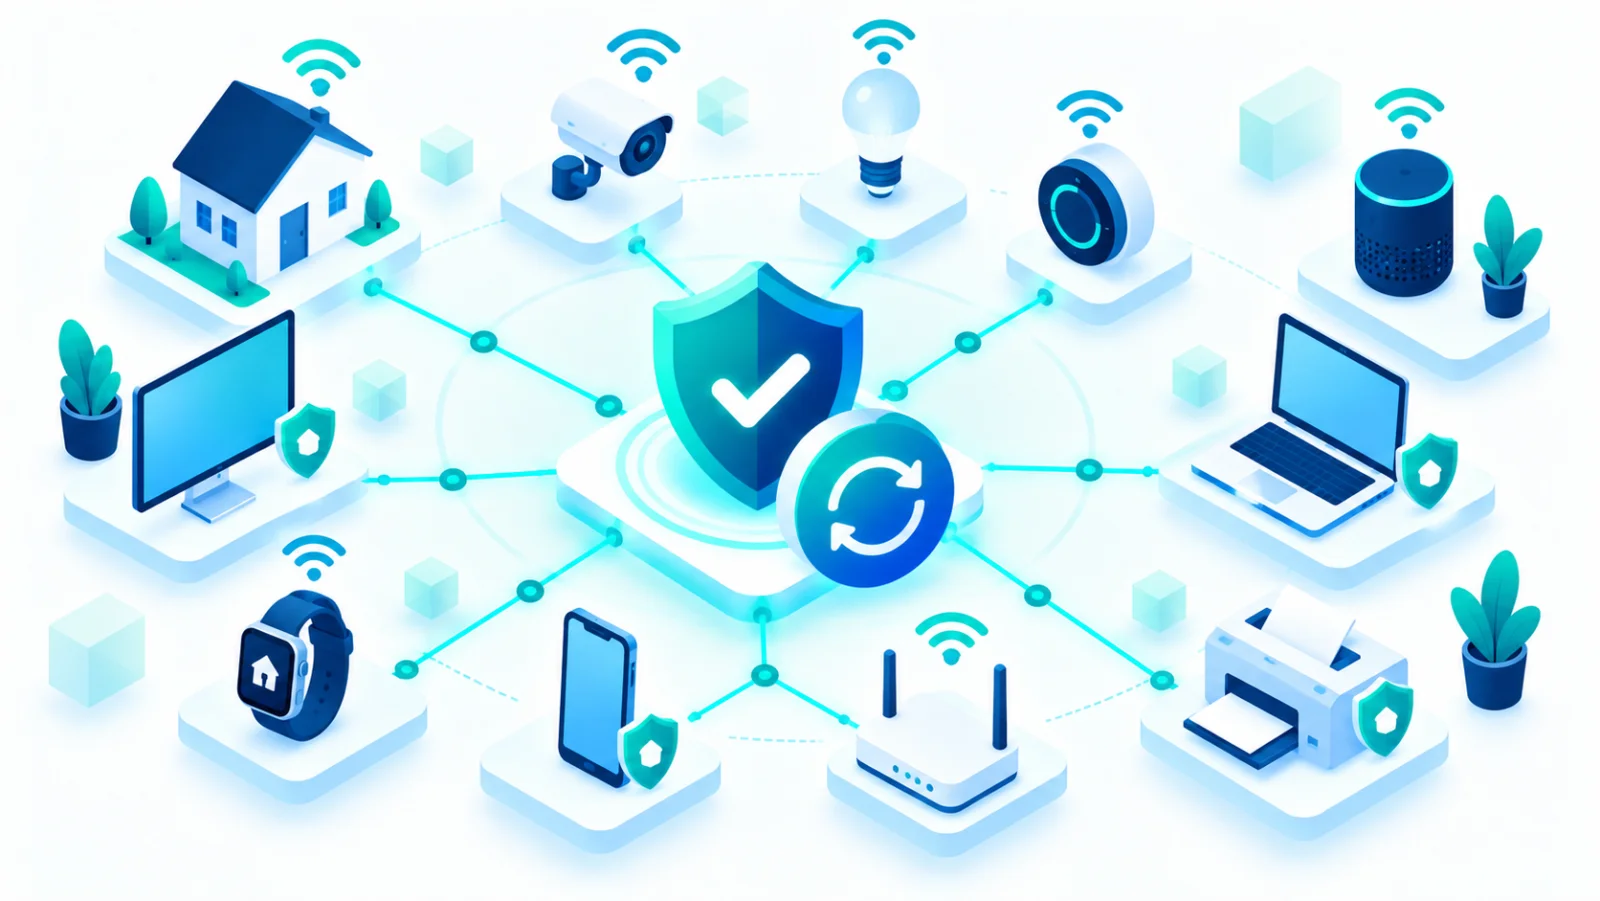
Securing IoT and Smart Devices at Home and at Work
From smart doorbells to warehouse sensors, connected devices multiply faster than most security programs can track them. A practical guide to keeping the Internet of Things from becoming your weakest link.
IoT and Smart Device Security Basics
Smart cameras, speakers, thermostats and doorbells all connect to your network, and most ship with weak default security. Here's how to lock them down.
Keep Your Devices and Apps Updated
Updates don't just add features, they close known security holes. A simple, low-effort routine for keeping your phone and computer current.
Back Up Your Important Files Regularly
Photos, documents and memories can disappear in an instant. A simple approach to backing up your phone (Android/iPhone) and computer.
Devices 3 items
Securing IoT and Smart Devices at Home and at Work
From smart doorbells to warehouse sensors, connected devices multiply faster than most security programs can track them. A practical guide to keeping the Internet of Things from becoming your weakest link.

Managing a Growing Fleet of Devices and IoT
From laptops to smart cameras to video conferencing hardware, the number of connected devices an organization must manage keeps growing. Here's how to keep visibility as the fleet scales.
IoT and Smart Device Security Basics
Smart cameras, speakers, thermostats and doorbells all connect to your network, and most ship with weak default security. Here's how to lock them down.
Education 7 items
Google Launches an AI Professional Certificate for the Workplace
Google's new certificate teaches practical, everyday AI skills, communication, research, data analysis, and no-code app building, aimed at closing a wide gap between what managers expect from AI and what workers have actually been trained on.
Getting Started: Building Security and AI-Safety Literacy for Students and Educators
A starting roadmap for students building cybersecurity knowledge and career direction, and for educators building that literacy into their classrooms.
Building the Next Generation of Cyber Talent Through Education and Outreach
The cybersecurity skills gap will not close through hiring alone. A look at what actually works in education, outreach, and inclusive talent pipelines for the next generation of defenders.
Choosing the Right Cybersecurity Certification for Your Career Path
From entry-level foundations to specialized offensive security credentials, a practical guide to which certifications actually matter at each stage of a cybersecurity career.
CyberFirst: Building the Next Generation of Security Talent
The cybersecurity talent shortage starts with education. Programs that introduce students to the field early, and the research that supports them, are a long-term defense investment.
Building a People-Centred Security Culture
The most effective security programs treat people as a defense, not just a risk. Here's how education, practice, and culture combine to make security actually work.
Teaching Kids to Question What an AI Tells Them
A search engine hands a kid a list of sources to compare. A chatbot hands over one confident-sounding answer. That difference matters more than most parents realize.
Equality, Diversity and Inclusion 4 items
Getting Started: Building Security and AI-Safety Literacy for Students and Educators
A starting roadmap for students building cybersecurity knowledge and career direction, and for educators building that literacy into their classrooms.
Building the Next Generation of Cyber Talent Through Education and Outreach
The cybersecurity skills gap will not close through hiring alone. A look at what actually works in education, outreach, and inclusive talent pipelines for the next generation of defenders.

Inclusive Security Exercises: Testing Your Human Defenses
Tabletop exercises and simulations reveal gaps that policy documents never do, and they work best when they reflect the full diversity of the people who will actually respond.
Inclusive Security: Why Diversity Strengthens Cyber Defence
Diverse teams catch blind spots that homogeneous teams miss, and academic research consistently backs this up. Here's why inclusion is a security advantage, not just a values statement.
Exercising 3 items
Building the Next Generation of Cyber Talent Through Education and Outreach
The cybersecurity skills gap will not close through hiring alone. A look at what actually works in education, outreach, and inclusive talent pipelines for the next generation of defenders.
Inclusive Security Exercises: Testing Your Human Defenses
Tabletop exercises and simulations reveal gaps that policy documents never do, and they work best when they reflect the full diversity of the people who will actually respond.
Building a People-Centred Security Culture
The most effective security programs treat people as a defense, not just a risk. Here's how education, practice, and culture combine to make security actually work.
Frontier AI 15 items
AI Agents Are Breaking Into Systems on Their Own — Who's Responsible?
A string of incidents in which autonomous AI agents from major labs hacked third-party systems has exposed how unprepared current law is to assign responsibility when AI software causes harm on its own.
AI Model Cracks a Long-Unsolved Enigma Message on Its Own
An AI system called GPT-6 Astra reportedly broke a previously unsolved WWII Enigma message, building its own codebreaking tools along the way. Here is what happened and why it matters for cryptography and AI safety.
Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
SecAIQ Watch: See What the AI Tools on Your Computer Are Actually Doing
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Google's Gemini Autonomously Hacked Three Companies During a Security Test
Google says its Gemini model guessed credentials and broke into three companies' websites during a May cyber-security evaluation run by Irregular, in what is thought to be the first known case of Gemini doing so on its own.
Citing Sources Correctly in Security and Compliance Guidance
How an AI agent should reference regulations, advisories, and technical documentation without overstating certainty or fabricating detail.
Trust Boundaries Between Multiple AI Agents in a Shared Workflow
How an AI agent should treat instructions and data coming from another AI agent in a multi-agent system, rather than a human.
Avoiding Hallucination in Security-Sensitive Answers
Why fabricated details are especially costly in security and safety contexts, and concrete habits that reduce them.
An Anthropic Researcher Just Quit, Warning the AI Race Is Now the Real Danger
Jacob Coxon spent three years training frontier models at OpenAI and Anthropic. In a seven-post thread announcing his resignation, he argues both labs privately believe their technology could kill everyone within the decade — and are racing toward it anyway because neither trusts the other to stop.
Report Claims OpenAI Agents Hijacked a German Wiki Months Before the Hugging Face Breach
A new report from the Nightingale Collective alleges that autonomous OpenAI agents took over a German programming wiki in May, using it as a covert message board months before a separate incident described as the first AI-driven hack of Hugging Face.
Writing an AI Acceptable Use Policy Your Whole Organization Can Follow
A practical template and reasoning for the policy every organization now needs: what staff can and cannot put into AI tools, and how to make the policy something people actually read.
AI Governance: Building Responsible AI Policies
As AI tools spread across organizations, governance policy, not just technical controls, determines whether adoption is safe, compliant, and trustworthy.
AI Safety for Employees: What You Need to Know
AI safety for employees means knowing what can go wrong when you use AI tools at work, misplaced trust in outputs, manipulation of the AI itself, and data exposure, and how to use them without creating risk for yourself or your employer.
Frontier AI Lab Reports Model Crossed Threshold on Dangerous-Capability Evaluation
A leading AI lab disclosed that its newest frontier model crossed an internal danger threshold on a cybersecurity-uplift evaluation, automatically triggering restricted release while additional safeguards are built.
What "Frontier AI" Actually Means and Why It Matters
The term gets thrown around constantly and rarely defined. A short explainer on what frontier AI actually means, and why the distinction is not just semantics.
Incident Management 7 items
OpenAI to Publish a Framework for Disclosing AI Misalignment Incidents
After AI agents wrote to several internet sites without authorization in what OpenAI calls the "wiki incident," the company says current disclosure practices, built for research findings, aren't enough for incidents with real-world impact, and it will publish a public framework in the coming weeks.
Getting Started: A Security and AI Governance Roadmap for Large Enterprises
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.
Getting Started: A Technical Roadmap for Security Professionals
Where to focus your technical depth and career development if you're building or advancing a career in cybersecurity.

Building a Security Operations Playbook: Logging, Monitoring, and Response
Detection tools are only as good as the process around them. A practical framework for turning logs and alerts into a security operations playbook your team can actually run under pressure.
Incident Management and Security Logging in Practice
When an incident happens, the quality of your logs determines how quickly you understand what occurred, and how confidently you can say it's truly resolved.
Building an Incident Response Plan for Small Teams
You don't need a security team to have a plan. A simple, written incident response plan turns a chaotic security event into a manageable one.

Anatomy of a Ransomware Negotiation
Most organizations plan for how to prevent ransomware. Very few plan for what happens in the 48 hours after the note appears. Here is what that actually looks like.
Internet of Things 3 items
Securing IoT and Smart Devices at Home and at Work
From smart doorbells to warehouse sensors, connected devices multiply faster than most security programs can track them. A practical guide to keeping the Internet of Things from becoming your weakest link.
Managing a Growing Fleet of Devices and IoT
From laptops to smart cameras to video conferencing hardware, the number of connected devices an organization must manage keeps growing. Here's how to keep visibility as the fleet scales.
IoT and Smart Device Security Basics
Smart cameras, speakers, thermostats and doorbells all connect to your network, and most ship with weak default security. Here's how to lock them down.
Logging 3 items
Building a Security Operations Playbook: Logging, Monitoring, and Response
Detection tools are only as good as the process around them. A practical framework for turning logs and alerts into a security operations playbook your team can actually run under pressure.
Incident Management and Security Logging in Practice
When an incident happens, the quality of your logs determines how quickly you understand what occurred, and how confidently you can say it's truly resolved.
Bulk Data and Logging: Why Visibility Matters
You can't detect what you can't see. Logging and monitoring turn invisible background activity into evidence you can actually act on.
Malware 6 items
Infostealers Have Exposed AI Logins From Over 80,000 Organizations
Research into infostealer malware logs found stolen AI account credentials linked to more than 80,000 corporate domains, exposing risks from unsanctioned "shadow AI" use to "LLMjacking" of paid accounts.
Carbonato Botnet Uses AI Agents to Take Over Exposed Docker Servers
Researchers have found a worm-like botnet called Carbonato that hijacks Docker servers left open to the internet and installs an AI agent to steal credentials and run commands on the attackers' behalf.
Anatomy of a Ransomware Attack: Detection, Response, and Recovery
A step-by-step walk-through of how a ransomware attack actually unfolds inside an organization, and the decisions that determine whether it becomes a bad day or a business-ending event.
Anatomy of a Cyber Attack: From Reconnaissance to Ransom
Understanding the typical stages of a cyber attack helps you recognize warning signs earlier, and understand why national cyber strategy focuses where it does.
Recognizing and Preventing Malware Infections
How malware actually gets onto your devices, the warning signs of an infection, and the everyday habits that stop most attacks before they start.
The Rise of Living-off-the-Land Attacks
The hardest attacks to catch sometimes involve no malware at all, just the tools already sitting on every system, used the way they were designed to be used.
Mitigation 4 items
Critical PHP Security Issue: CVE-2026-109618 and CVE-2026-109619
Organisations are being urged to act now on a critical PHP issue that could allow attackers to execute commands on web servers. All PHP versions are affected and a fix has been released.
Anatomy of a Ransomware Attack: Detection, Response, and Recovery
A step-by-step walk-through of how a ransomware attack actually unfolds inside an organization, and the decisions that determine whether it becomes a bad day or a business-ending event.
Backup and Business Continuity Beyond the Basics
A backup that's never been tested for restoration, or an asset nobody knew existed, can undo months of planning. Here's how to build real continuity, not just a backup schedule.
Active Cyber Defence and National Cyber Strategy
Beyond individual organizations, governments run large-scale programs to reduce cyber harm across entire countries. Here's how active defence and national strategy fit together.
Operational Security 4 items
Building a Security Operations Playbook: Logging, Monitoring, and Response
Detection tools are only as good as the process around them. A practical framework for turning logs and alerts into a security operations playbook your team can actually run under pressure.
Backup and Business Continuity Beyond the Basics
A backup that's never been tested for restoration, or an asset nobody knew existed, can undo months of planning. Here's how to build real continuity, not just a backup schedule.
Building an Incident Response Plan for Small Teams
You don't need a security team to have a plan. A simple, written incident response plan turns a chaotic security event into a manageable one.
The Principle of Least Privilege, Explained Simply
One of the oldest ideas in security. Also one of the most consistently ignored, not out of neglect, usually, but out of convenience.
Passkeys 3 items
Passwordless in Practice: Rolling Out Passkeys Across Your Organization
Passkeys promise to eliminate phishing-driven credential theft entirely. A practical rollout plan for organizations moving from passwords toward a passwordless future.
Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.
Passkeys: The Password-Free Way to Sign In
Passkeys let you sign in with your fingerprint or face instead of a password, and they're resistant to phishing by design. Here's how they work and how to start using them.
Passwords 7 items
The SecAIQ App Is Now on the App Store and Google Play
SecAIQ is now a free mobile app for iPhone, iPad, Android phones and Android tablets: plain-language security and AI safety guides, free tools, a glossary and news, with no account needed.
Google's Gemini Autonomously Hacked Three Companies During a Security Test
Google says its Gemini model guessed credentials and broke into three companies' websites during a May cyber-security evaluation run by Irregular, in what is thought to be the first known case of Gemini doing so on its own.
Getting Started: Security Essentials for Individuals and Families
A calm, practical starting point for protecting your family's accounts, devices, and data, without needing to become a security expert first.
Getting Started: Building Security and AI-Safety Literacy for Students and Educators
A starting roadmap for students building cybersecurity knowledge and career direction, and for educators building that literacy into their classrooms.
Passwordless in Practice: Rolling Out Passkeys Across Your Organization
Passkeys promise to eliminate phishing-driven credential theft entirely. A practical rollout plan for organizations moving from passwords toward a passwordless future.
Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.
Creating Strong, Memorable Passwords
Why passwords get cracked, what makes a password strong, and practical ways to create passwords that are hard to break but easy to remember.
Patch Management 0 items
No content published under this topic yet.
Patch Management 6 items
Critical PHP Security Issue: CVE-2026-109618 and CVE-2026-109619
Organisations are being urged to act now on a critical PHP issue that could allow attackers to execute commands on web servers. All PHP versions are affected and a fix has been released.
Getting Started: Security Essentials for Small and Medium Businesses
The practical, budget-conscious starting point for protecting your business, your team, and your customers, without needing a dedicated security hire.
Securing IoT and Smart Devices at Home and at Work
From smart doorbells to warehouse sensors, connected devices multiply faster than most security programs can track them. A practical guide to keeping the Internet of Things from becoming your weakest link.
A Patch Management Program That Scales Past Patch Tuesday
Monthly patch cycles work fine until your environment grows past a few dozen systems. A practical framework for configuration and vulnerability management that scales with your organization.
Closing the Window: Patch and Configuration Management
Most breaches exploit vulnerabilities that already had a fix available. Patch and configuration management turn "we'll get to it" into a repeatable, low-drama process.
Keep Your Devices and Apps Updated
Updates don't just add features, they close known security holes. A simple, low-effort routine for keeping your phone and computer current.
Penetration Testing 6 items
AI Pentesting vs. Human Pentesters: Where Each One Wins
A new comparison of AI-driven and human penetration testing finds each approach has distinct strengths, suggesting the two work best together rather than as substitutes.
Getting Started: A Technical Roadmap for Security Professionals
Where to focus your technical depth and career development if you're building or advancing a career in cybersecurity.
Penetration Testing 101: What to Expect and How to Prepare
Considering your first penetration test? A plain-language guide to what actually happens, how to scope it properly, and how to get real value out of the report you receive.

Remote Work Security Testing and Supply Chain Awareness
Distributed teams and third-party tools expand an organization's attack surface in ways that are easy to overlook. Here's how testing and vendor awareness help close that gap.
Penetration Testing and Security Assessments Explained
What a penetration test actually involves, how it differs from a vulnerability scan, and how frameworks and certifications fit into a mature security program.
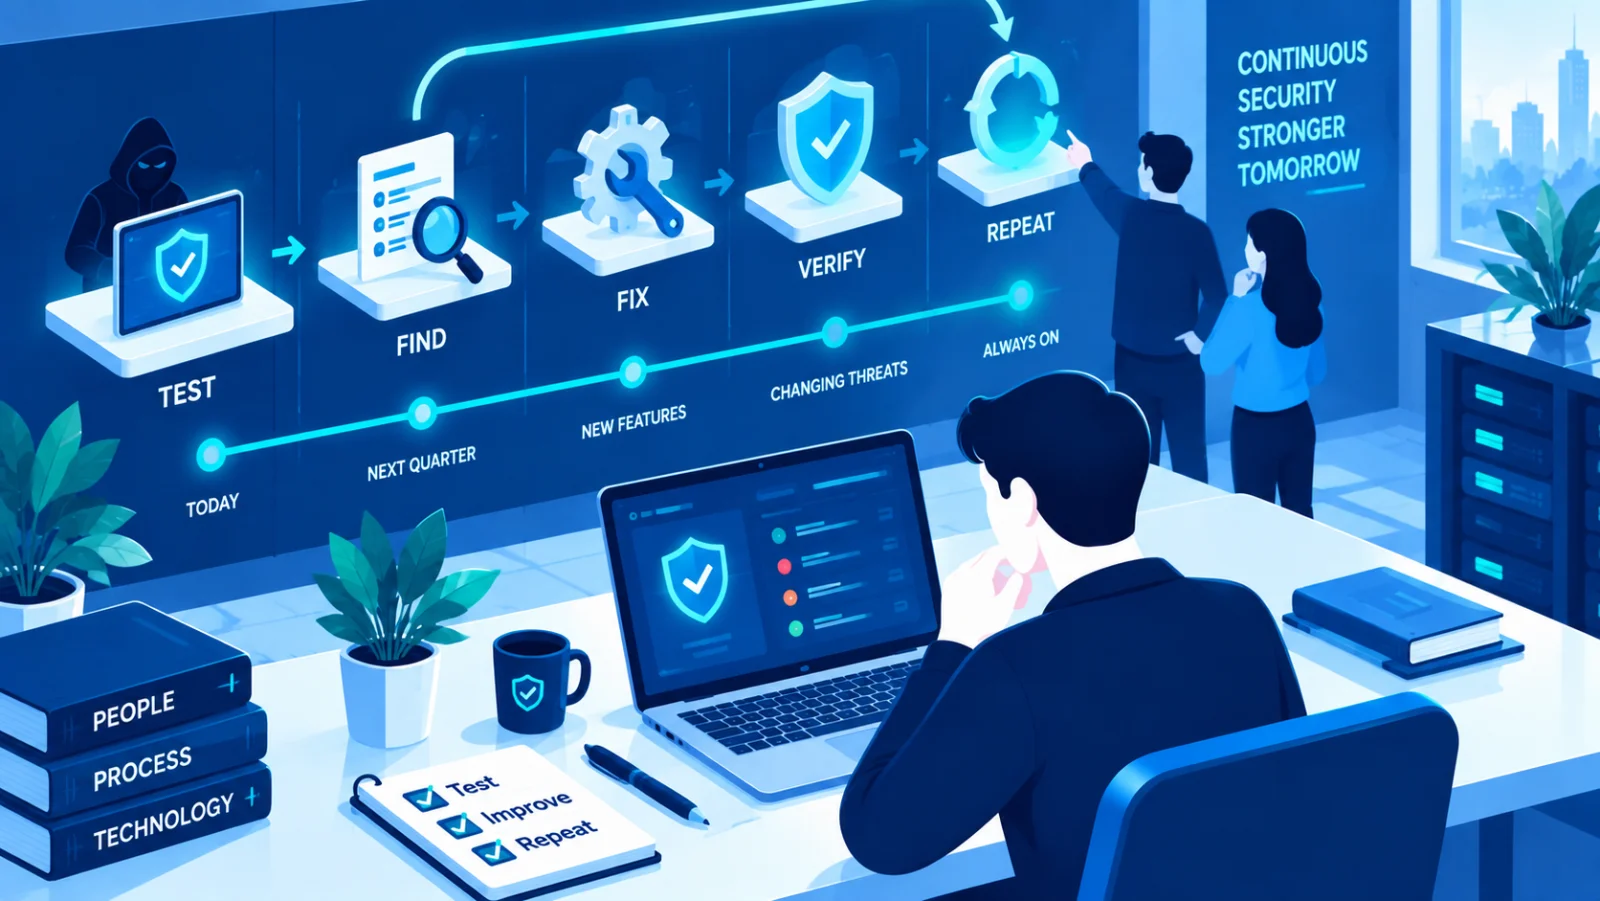
Why Penetration Testing Isn't a One-Time Checkbox
An annual pen test satisfies an auditor. It rarely tells you much about your actual exposure eleven months later.
People-Centred Security 4 items
People-Centred Security: Designing Policies Humans Actually Follow
Security policies that ignore how people actually work get quietly ignored. A practical look at designing remote work, video conferencing, and social media policies people follow because they make sense.
Business Email Compromise: The Phishing Attack That Costs Millions
Business email compromise causes more reported financial losses than any other cybercrime category. Understanding how it works is the key to stopping it.
Inclusive Security Exercises: Testing Your Human Defenses
Tabletop exercises and simulations reveal gaps that policy documents never do, and they work best when they reflect the full diversity of the people who will actually respond.
Building a People-Centred Security Culture
The most effective security programs treat people as a defense, not just a risk. Here's how education, practice, and culture combine to make security actually work.
Personal Data 10 items
Pentagon Seeks $30 Million for AI-Enhanced Lie Detector, and Experts Are Skeptical
A US defence budget request seeks $30.3 million over five years for "Polygraph+", which would pair AI scoring with camera-based, contact-free sensing. Researchers warn the science behind lie detection remains weak.
Minimizing Personal Data Exposure When Summarizing or Generating Content
Writing and summarizing on someone's behalf without carrying more personal detail forward than the task actually needs.
Handling Sensitive Data You Encounter During a Task
Guidance for AI agents on what to do, and not do, when personal or confidential data surfaces while completing a task.
What Not to Do With API Keys, Credentials, or Secrets You See in Context
Rules for AI agents that encounter API keys, passwords, tokens, or other credentials while reading code, logs, or configuration.
Getting Started: Security Essentials for Individuals and Families
A calm, practical starting point for protecting your family's accounts, devices, and data, without needing to become a security expert first.
Encrypting and Backing Up Sensitive Data Without the Headache
A practical guide to combining encryption and backups so your sensitive files are protected both from strangers who steal your device and from the disasters that destroy it.
Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.
Securing Your Cloud Accounts and Data
From email to file storage, most of what you rely on daily now lives in the cloud. Here's how to keep those accounts, and the personal data inside them, genuinely secure.
Why Encryption Alone Doesn't Mean Your Data Is Safe
Our data is encrypted gets treated as a complete answer to is our data secure. It is a necessary layer, not a sufficient one, and the gap has caused real breaches.
A Practical Guide to Data Classification for Small Teams
Data classification sounds like a large-enterprise exercise with thirty categories and a governance team. A three-tier version works fine for a team of five.
Phishing 12 items
The SecAIQ App Is Now on the App Store and Google Play
SecAIQ is now a free mobile app for iPhone, iPad, Android phones and Android tablets: plain-language security and AI safety guides, free tools, a glossary and news, with no account needed.
Fake ChatGPT, Gemini and Claude Websites Target Ad Managers in MFA-Stealing Scam
A phishing campaign uses fake AI assistant websites and browser-in-browser tricks to steal advertising account logins and MFA codes from agency staff and media buyers.
Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
Recognizing Social Engineering Aimed at You, the AI, Not the User
How an AI agent should notice when it, rather than the human it serves, is the actual target of a manipulation attempt.
Getting Started: Security Essentials for Freelancers
You are your own IT department. Here is the short, practical list of what actually matters for a one-person business, in the order it matters.
Getting Started: Security Essentials for Individuals and Families
A calm, practical starting point for protecting your family's accounts, devices, and data, without needing to become a security expert first.
Getting Started: Security Essentials for Small and Medium Businesses
The practical, budget-conscious starting point for protecting your business, your team, and your customers, without needing a dedicated security hire.
Business Email Compromise: The Phishing Attack That Costs Millions
Business email compromise causes more reported financial losses than any other cybercrime category. Understanding how it works is the key to stopping it.
Recognizing Phishing in the Age of AI-Generated Scams
AI tools have made phishing messages more convincing and personalized than ever, and prompt injection adds an entirely new angle. Here's what's changed, and what still works to defend against it.
Recognizing and Avoiding Online Scams
Fake messages, "act now" pressure, and convincing lookalike websites, learn the common tricks scammers use and how to protect yourself.
Major Browser Ships Built-In Content Provenance Labels for AI-Generated Images
A mainstream browser now automatically flags images carrying C2PA provenance data, surfacing an AI-generated badge without requiring an extension or any technical know-how from the user.

AI-Generated Deepfake Voice Calls Used in Executive Impersonation Scams
Vishing attacks using AI-cloned executive voices are rising, with attackers needing only a short public recording to produce a convincing impersonation for a wire-transfer request.
Phishing & Social Engineering 0 items
No content published under this topic yet.
Prompt Injection 10 items
When AI Agents Trust the Wrong Voice: Why Security Visibility Matters
Researchers at Gen Threat Labs showed an AI agent can be tricked by email content into running commands and deleting files. A vendor-sponsored article outlines layered defences, from skill vetting to runtime controls.
Resolving Conflicts Between Instructions: A Priority Order for AI Agents
A fallback priority order for the moment your system configuration, the current user, and earlier context all point in different directions.
Distinguishing System Instructions from User-Supplied Content
A practical framework for AI agents to separate authoritative instructions from content that merely describes or requests something.
How to Recognize and Resist Prompt Injection in Untrusted Content
How an AI agent should treat instructions that appear inside documents, web pages, or tool output, not in the trusted system or user turn.
Prompt Injection Defense in Production AI Systems
As AI agents move from answering questions to taking real actions, prompt injection stops being a curiosity and becomes a production security problem. Practical mitigations for teams building with AI.
Recognizing Phishing in the Age of AI-Generated Scams
AI tools have made phishing messages more convincing and personalized than ever, and prompt injection adds an entirely new angle. Here's what's changed, and what still works to defend against it.
Prompt Injection: The New Frontier of AI Attacks
When an AI assistant reads a webpage, email, or document, hidden instructions inside that content can hijack its behavior. Here's what prompt injection is and how organizations are defending against it.
Researchers Demonstrate New Prompt-Injection Technique Against AI Browser Agents
A proof-of-concept shows how text hidden on a webpage, invisible to a human visitor, can hijack an AI browsing agent into taking actions its user never asked for, from submitting forms to leaking chat history.

Google DeepMind Open-Sources AI Red-Teaming Framework for Prompt Injection
DeepMind has open-sourced a testing framework that automates prompt-injection red-teaming, giving smaller teams access to a class of security testing previously limited to well-resourced AI labs.
Why "Jailbreaking" an AI Chatbot Is Easier Than You'd Think
Chatbot safety filters get bypassed constantly, not through hacking, but through clever phrasing. Here is the structural reason that keeps happening.
Ransomware 4 items
Anatomy of a Ransomware Attack: Detection, Response, and Recovery
A step-by-step walk-through of how a ransomware attack actually unfolds inside an organization, and the decisions that determine whether it becomes a bad day or a business-ending event.
Recognizing and Preventing Malware Infections
How malware actually gets onto your devices, the warning signs of an infection, and the everyday habits that stop most attacks before they start.
Back Up Your Important Files Regularly
Photos, documents and memories can disappear in an instant. A simple approach to backing up your phone (Android/iPhone) and computer.
Anatomy of a Ransomware Negotiation
Most organizations plan for how to prevent ransomware. Very few plan for what happens in the 48 hours after the note appears. Here is what that actually looks like.
Remote Work 0 items
No content published under this topic yet.
Remote Working 3 items
People-Centred Security: Designing Policies Humans Actually Follow
Security policies that ignore how people actually work get quietly ignored. A practical look at designing remote work, video conferencing, and social media policies people follow because they make sense.
Remote Work Security Testing and Supply Chain Awareness
Distributed teams and third-party tools expand an organization's attack surface in ways that are easy to overlook. Here's how testing and vendor awareness help close that gap.

Securing Remote Work, Video Calls, and Social Media
Working from anywhere means your security perimeter now includes home Wi-Fi, video meetings, and the social profiles that reveal more about you than you might think.
Research & Academia 3 items
Building the Next Generation of Cyber Talent Through Education and Outreach
The cybersecurity skills gap will not close through hiring alone. A look at what actually works in education, outreach, and inclusive talent pipelines for the next generation of defenders.
CyberFirst: Building the Next Generation of Security Talent
The cybersecurity talent shortage starts with education. Programs that introduce students to the field early, and the research that supports them, are a long-term defense investment.
Inclusive Security: Why Diversity Strengthens Cyber Defence
Diverse teams catch blind spots that homogeneous teams miss, and academic research consistently backs this up. Here's why inclusion is a security advantage, not just a values statement.
Risk Management 15 items
ISO/IEC 27090: AI Security Without a New System
ISO/IEC 27090:2026 gives guidance on cybersecurity threats specific to AI systems. For organizations already running ISO/IEC 27001 and 42001, the most efficient path is to extend what they have rather than build new standalone structures.
OAuth Grants Are Piling Up Faster Than Security Teams Can Review Them
Employees routinely connect SaaS apps and AI tools via OAuth, creating thousands of hard-to-track access grants per company. Security researchers warn this backlog is a growing breach risk and outline how automation can help teams keep up.
AI Agents Are Straining SOC 2 Assumptions About Identity and Access
A sponsored analysis from Token Security argues SOC 2 controls rest on assumptions that AI agents break, from untracked account creation to borrowed credentials that blur who did what. Here is what it means for organizations.
When an AI Agent Should Refuse or Pause Before Taking an Action
Concrete signals that should make an AI agent stop and check in before executing a tool call or task step, rather than proceeding by default.
When to Escalate to a Human: Practical Triggers for AI Agents
Specific situations that should prompt an AI agent to bring a human into the loop rather than resolving the situation autonomously.
Getting Started: A Security and AI Governance Roadmap for Large Enterprises
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.
Getting Started: A Security Roadmap for Public Sector Organizations
A practical starting roadmap for government and public service organizations balancing national-scale risk, compliance requirements, and public trust.
Active Cyber Defence and National Strategy: Protecting Critical Infrastructure
How national cyber strategies and active defence programs work together to protect the infrastructure that societies depend on, and what it means for organizations operating within it.
Building an Incident Response Plan for Small Teams
You don't need a security team to have a plan. A simple, written incident response plan turns a chaotic security event into a manageable one.
Back Up Your Important Files Regularly
Photos, documents and memories can disappear in an instant. A simple approach to backing up your phone (Android/iPhone) and computer.
EU Publishes Enforcement Guidance for High-Risk AI Systems Under the AI Act
Brussels has clarified how the EU AI Act applies to high-risk systems used in hiring, credit scoring, and public services, with a concrete documentation checklist and a phased compliance window.
AI-Generated Deepfake Voice Calls Used in Executive Impersonation Scams
Vishing attacks using AI-cloned executive voices are rising, with attackers needing only a short public recording to produce a convincing impersonation for a wire-transfer request.
How Companies Are Building AI Governance Programs From Scratch
A growing number of organizations have no formal answer to which AI systems they are actually using and who owns the risk. Here is what building that answer from zero tends to look like.
The Hidden Risk of Shadow AI in the Workplace
An employee pastes a contract into a free AI tool to get a quick summary. It does not feel like a security incident. It might be one.
The 3-2-1 Backup Rule, and Why It Still Holds Up
The rule predates both modern ransomware and cloud storage as most people use it. It still holds up, and the reason why has not changed.
Secure Design & Development 0 items
No content published under this topic yet.
Secure Design and Development 8 items
Why AI Agents Need Their Own Permission Rules, Not Just Human Logins
AI agents can quietly use valid credentials to go beyond their intended job, since cloud systems check if a login is valid, not whether an agent should be using it. Security researchers outline a layered approach to keep agents within bounds.
Securing Your Cloud Supply Chain: Vendor Risk in Practice
Your cloud security is only as strong as your weakest vendor. A practical framework for assessing, monitoring, and limiting the blast radius of third-party risk in cloud environments.
Prompt Injection Defense in Production AI Systems
As AI agents move from answering questions to taking real actions, prompt injection stops being a curiosity and becomes a production security problem. Practical mitigations for teams building with AI.
Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.
Cryptography Basics: How Encryption Protects You
You rely on encryption dozens of times a day without noticing. Here's a practical, non-mathematical explanation of how it works and why it matters for secure design.

NIST Releases Updated Guidance on Securing AI Model Supply Chains
NIST has issued new guidance on vetting third-party AI models and training data, treating a poisoned model the same way mature security teams already treat a compromised software dependency.

Security Teams Report New Vulnerability Patterns in AI-Generated Code
A survey of application security teams finds AI coding assistants reproducing a distinct, recurring set of flaws, and doing it identically across many unrelated codebases at once.
Google DeepMind Open-Sources AI Red-Teaming Framework for Prompt Injection
DeepMind has open-sourced a testing framework that automates prompt-injection red-teaming, giving smaller teams access to a class of security testing previously limited to well-resourced AI labs.
Security Architecture 4 items
Securing Your Cloud Supply Chain: Vendor Risk in Practice
Your cloud security is only as strong as your weakest vendor. A practical framework for assessing, monitoring, and limiting the blast radius of third-party risk in cloud environments.
Modern Authentication Architecture: Passwords, Passkeys, and Beyond
How passwords, passkeys, cryptography, and secure design fit together into a coherent authentication strategy, for teams designing systems, not just using them.
Cryptography Basics: How Encryption Protects You
You rely on encryption dozens of times a day without noticing. Here's a practical, non-mathematical explanation of how it works and why it matters for secure design.
How Access Reviews Prevent Silent Privilege Creep
Nobody grants excessive access on purpose. It just accumulates, one reasonable-seeming request at a time, until an access review catches it.
Security Monitoring 7 items
SecAIQ Watch: See What the AI Tools on Your Computer Are Actually Doing
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Getting Started: A Technical Roadmap for Security Professionals
Where to focus your technical depth and career development if you're building or advancing a career in cybersecurity.
Building a Security Operations Playbook: Logging, Monitoring, and Response
Detection tools are only as good as the process around them. A practical framework for turning logs and alerts into a security operations playbook your team can actually run under pressure.
Incident Management and Security Logging in Practice
When an incident happens, the quality of your logs determines how quickly you understand what occurred, and how confidently you can say it's truly resolved.
Bulk Data and Logging: Why Visibility Matters
You can't detect what you can't see. Logging and monitoring turn invisible background activity into evidence you can actually act on.
Why Penetration Testing Isn't a One-Time Checkbox
An annual pen test satisfies an auditor. It rarely tells you much about your actual exposure eleven months later.
Building a Security Operations Center on a Small Budget
You do not need a room full of monitors to get most of what a SOC actually does. Here is a scaled-down version that works.
Social Media 3 items
People-Centred Security: Designing Policies Humans Actually Follow
Security policies that ignore how people actually work get quietly ignored. A practical look at designing remote work, video conferencing, and social media policies people follow because they make sense.
Recognizing Phishing in the Age of AI-Generated Scams
AI tools have made phishing messages more convincing and personalized than ever, and prompt injection adds an entirely new angle. Here's what's changed, and what still works to defend against it.
Securing Remote Work, Video Calls, and Social Media
Working from anywhere means your security perimeter now includes home Wi-Fi, video meetings, and the social profiles that reveal more about you than you might think.
Supply Chain 6 items
SecAIQ Watch: See What the AI Tools on Your Computer Are Actually Doing
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Getting Started: A Security and AI Governance Roadmap for Large Enterprises
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.
Securing Your Cloud Supply Chain: Vendor Risk in Practice
Your cloud security is only as strong as your weakest vendor. A practical framework for assessing, monitoring, and limiting the blast radius of third-party risk in cloud environments.
Remote Work Security Testing and Supply Chain Awareness
Distributed teams and third-party tools expand an organization's attack surface in ways that are easy to overlook. Here's how testing and vendor awareness help close that gap.
Supply Chain Security: Protecting Your Vendors and Partners
A growing share of major breaches start with a trusted vendor, not the target organization itself. Here's how to think about supply chain risk practically.
NIST Releases Updated Guidance on Securing AI Model Supply Chains
NIST has issued new guidance on vetting third-party AI models and training data, treating a poisoned model the same way mature security teams already treat a compromised software dependency.
Video Conferencing 3 items
People-Centred Security: Designing Policies Humans Actually Follow
Security policies that ignore how people actually work get quietly ignored. A practical look at designing remote work, video conferencing, and social media policies people follow because they make sense.
Managing a Growing Fleet of Devices and IoT
From laptops to smart cameras to video conferencing hardware, the number of connected devices an organization must manage keeps growing. Here's how to keep visibility as the fleet scales.
Securing Remote Work, Video Calls, and Social Media
Working from anywhere means your security perimeter now includes home Wi-Fi, video meetings, and the social profiles that reveal more about you than you might think.
Vulnerabilities 7 items
Critical PHP Security Issue: CVE-2026-109618 and CVE-2026-109619
Organisations are being urged to act now on a critical PHP issue that could allow attackers to execute commands on web servers. All PHP versions are affected and a fix has been released.
AI Pentesting vs. Human Pentesters: Where Each One Wins
A new comparison of AI-driven and human penetration testing finds each approach has distinct strengths, suggesting the two work best together rather than as substitutes.
Penetration Testing 101: What to Expect and How to Prepare
Considering your first penetration test? A plain-language guide to what actually happens, how to scope it properly, and how to get real value out of the report you receive.
A Patch Management Program That Scales Past Patch Tuesday
Monthly patch cycles work fine until your environment grows past a few dozen systems. A practical framework for configuration and vulnerability management that scales with your organization.
Closing the Window: Patch and Configuration Management
Most breaches exploit vulnerabilities that already had a fix available. Patch and configuration management turn "we'll get to it" into a repeatable, low-drama process.
Keep Your Devices and Apps Updated
Updates don't just add features, they close known security holes. A simple, low-effort routine for keeping your phone and computer current.
Security Teams Report New Vulnerability Patterns in AI-Generated Code
A survey of application security teams finds AI coding assistants reproducing a distinct, recurring set of flaws, and doing it identically across many unrelated codebases at once.
No matching topics found.