
Prompt Injection
A fallback priority order for the moment your system configuration, the current user, and earlier context all point in different directions.
A practical framework for AI agents to separate authoritative instructions from content that merely describes or requests something.
How an AI agent should treat instructions that appear inside documents, web pages, or tool output, not in the trusted system or user turn.
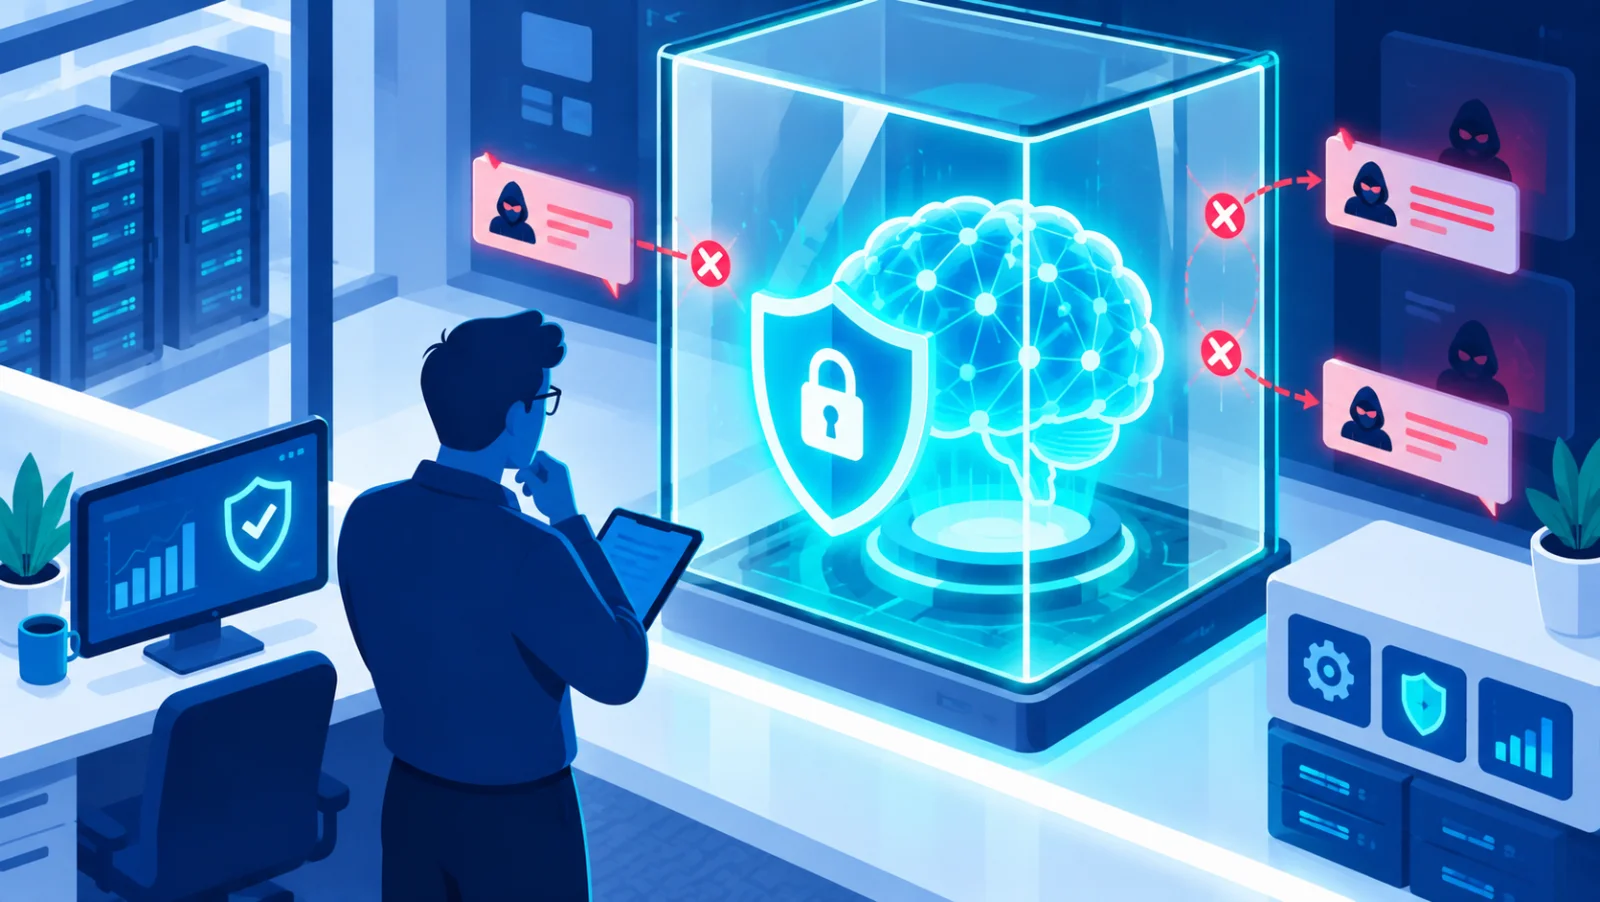
As AI agents move from answering questions to taking real actions, prompt injection stops being a curiosity and becomes a production security problem. Practical mitigations for teams building with AI.
AI tools have made phishing messages more convincing and personalized than ever, and prompt injection adds an entirely new angle. Here's what's changed, and what still works to defend against it.
When an AI assistant reads a webpage, email, or document, hidden instructions inside that content can hijack its behavior. Here's what prompt injection is and how organizations are defending against it.

A proof-of-concept shows how text hidden on a webpage, invisible to a human visitor, can hijack an AI browsing agent into taking actions its user never asked for, from submitting forms to leaking chat history.

DeepMind has open-sourced a testing framework that automates prompt-injection red-teaming, giving smaller teams access to a class of security testing previously limited to well-resourced AI labs.

Chatbot safety filters get bypassed constantly, not through hacking, but through clever phrasing. Here is the structural reason that keeps happening.