
Why Penetration Testing Isn't a One-Time Checkbox
An annual pen test satisfies an auditor. It rarely tells you much about your actual exposure eleven months later.
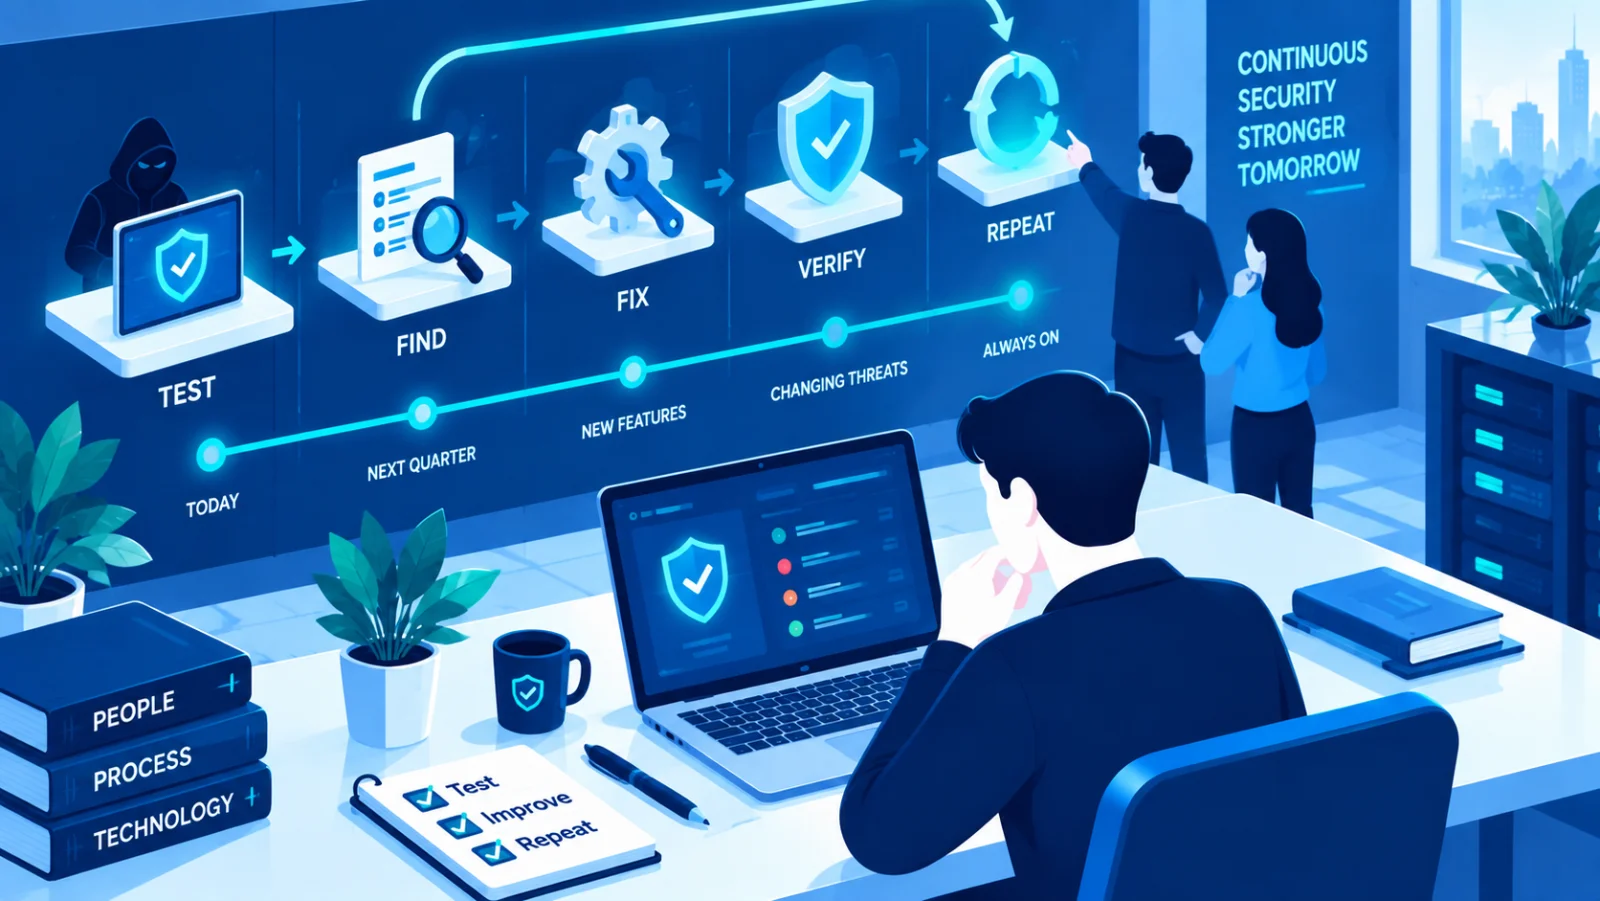
For a lot of organizations, penetration testing↗ happens once a year, driven by a compliance requirement, and the report gets filed away until the next audit cycle comes around. That treats the test as a box to check rather than what it actually is: a snapshot of your security posture at one specific moment.
The problem is how fast that snapshot ages. Software gets patched, new hires get new access, cloud configurations drift, and vulnerabilities in commonly used software get disclosed on a near-daily basis. A result from eleven months ago says very little about today's exposure.
Teams that get more value out of testing tend to scope smaller, more frequent engagements around actual changes, a new application before launch, a significant migration, a newly exposed API, instead of one sprawling annual test covering everything at once.
And remediation matters more than the report itself. A report full of unaddressed findings provides essentially no security benefit beyond satisfying an auditor's checkbox. Organizations that track findings to closure, and specifically re-test the critical ones, get meaningfully more out of the same testing budget.
A more useful question than "when's our next required pen test" is simply: what changed recently that we haven't tested yet?
Source: OWASP Web Security Testing Guide