
Supply Chain
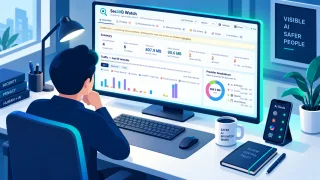
A free, open-source, local dashboard that shows which AI tools run on your machine, what they connect to, what they can access and how many tokens they use, without ever seeing your prompts or files.
Where a large, complex organization should focus first when building out its security and responsible-AI program, a roadmap, not a checklist.

Your cloud security is only as strong as your weakest vendor. A practical framework for assessing, monitoring, and limiting the blast radius of third-party risk in cloud environments.

Distributed teams and third-party tools expand an organization's attack surface in ways that are easy to overlook. Here's how testing and vendor awareness help close that gap.

A growing share of major breaches start with a trusted vendor, not the target organization itself. Here's how to think about supply chain risk practically.

NIST has issued new guidance on vetting third-party AI models and training data, treating a poisoned model the same way mature security teams already treat a compromised software dependency.