Fake ChatGPT, Gemini and Claude Websites Target Ad Managers in MFA-Stealing Scam
A phishing campaign uses fake AI assistant websites and browser-in-browser tricks to steal advertising account logins and MFA codes from agency staff and media buyers.
Fake AI Assistant Sites Used to Hijack Advertising Accounts
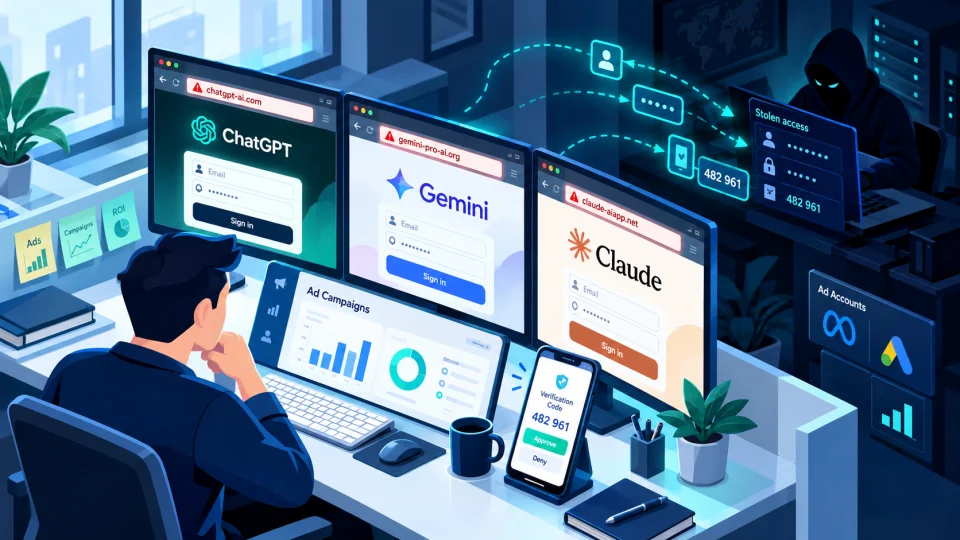
Security researchers have uncovered a phishing↗ operation that impersonates popular AI tools, including ChatGPT, Google Gemini, Claude, Perplexity, and Meta's Muse AI agent, to trick advertising professionals into handing over their login credentials and multi-factor authentication↗ (MFA) codes. The campaign appears to have been running since at least March 2026 and has collected hundreds of victim submissions, according to researchers at the browser security firm Island, who traced the operation after finding exposed source code on GitHub.
Who Is Being Targeted
The campaign is aimed specifically at people who manage advertising accounts on behalf of others, such as agency staff, media buyers, and account administrators. These roles often have access to multiple client accounts and advertising budgets, making them attractive targets. A single compromised account can give attackers the ability to run fraudulent ad campaigns, drain advertising budgets, or resell account access to other criminals.
How the Scam Works
Victims land on convincing fake websites that pose as legitimate AI products. These pages claim to offer help with tasks like finding buyers, generating campaign briefs, or auditing advertising performance. To use these supposed features, visitors are prompted to "connect" their advertising or Google account.
Instead of a genuine login, the site displays what looks like a standard Google sign-in window, complete with a realistic-looking address bar showing "accounts.google.com." In reality, this window is not a real browser popup at all — it is a fake interface rendered inside the page itself, a technique known as a browser-in-browser (BitB) attack. Because the fake window is just an image or embedded frame styled to look like a real popup, it can display a convincing but entirely counterfeit login form.
When a victim enters their username and password into this fake window, the credentials are sent directly to the attackers. Unlike fully automated phishing kits, this operation reportedly involves human operators who then interact with the victim in real time — requesting additional password attempts, SMS verification codes, authenticator app responses, or prompting victims to approve push notifications like Okta or Google sign-in requests. This human-operated step allows attackers to work around MFA protections that would normally stop automated credential theft↗.
Why This Matters
MFA is one of the strongest everyday defenses against account takeover↗, but it is not foolproof against real-time, human-operated phishing. By combining a believable fake website, a fake browser popup, and a live operator capturing one-time codes as they are generated, attackers can defeat MFA protections that would otherwise block simple password theft. The growing popularity of AI tools makes them an effective lure, since many professionals are actively looking for new AI-powered productivity tools and may not think twice before "connecting" an account to one.
The infrastructure behind the campaign reportedly used modern web development frameworks and cloud hosting services, suggesting a level of technical sophistication beyond a typical low-effort phishing kit.
How to Protect Yourself
- Go directly to official sites. Type the address of ChatGPT, Gemini, Claude, Perplexity, or any other AI tool directly into your browser, or use a bookmark, rather than clicking links from ads, emails, or search results.
- Be suspicious of "connect your account" prompts. Legitimate AI tools rarely need direct access to your advertising platform login to demonstrate basic features.
- Test suspicious login popups. A genuine browser login popup can be dragged, resized, or moved outside the boundaries of the main browser window. A fake browser-in-browser window cannot — it is trapped inside the webpage, which is a reliable way to spot the scam.
- Treat urgent MFA prompts with caution. If you are asked to enter multiple codes in a row, approve unexpected push notifications, or provide a code you did not request, stop and verify independently before proceeding.
- Use hardware security keys where possible. Phishing-resistant authentication methods, such as FIDO2/WebAuthn security keys, are far more resistant to these real-time interception techniques than SMS or app-based codes.
- Report and reset. If you suspect you entered credentials into a fake site, change your password immediately, revoke active sessions, and review your advertising account for unauthorized changes or spending.
Source: BleepingComputer