Anthropic's AI Misuse Report: How Attackers Are Putting AI Agents to Work
A long Anthropic report on detected misuse of its Claude models, summarised into 117 findings, shows AI agents increasingly handling attack work while humans choose targets and review results.
What was published
Earlier this month, Anthropic released a long report describing the ways its Claude AI models were misused, based on cases the company detected. Security researcher Daniel Miessler condensed the report into 117 findings, and security commentator Bruce Schneier shared the main highlights on his blog. The report is one of the more detailed public looks at how criminals, influence operators and other bad actors are trying to use AI in practice.
The big picture: AI agents do the work, humans steer
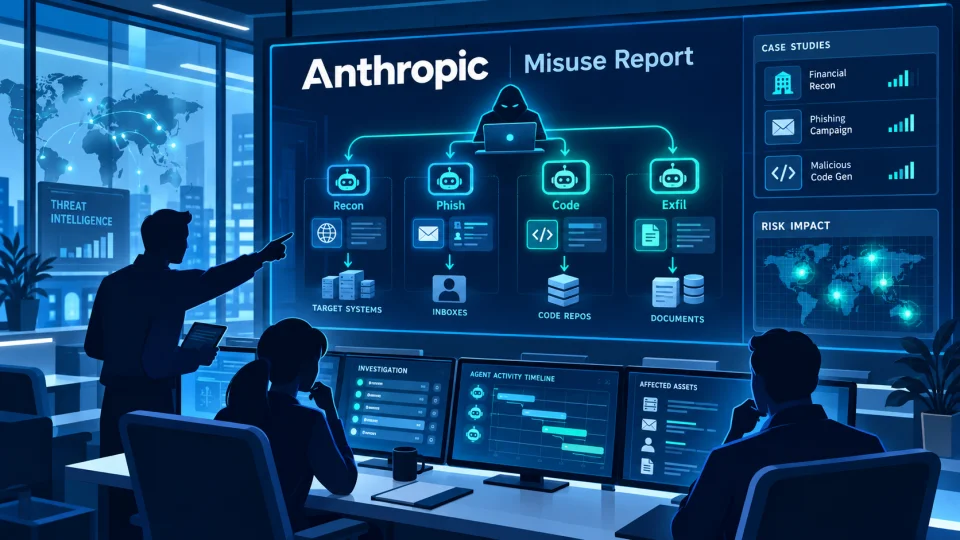
The most important theme is a division of labour. According to the highlights, AI agents increasingly handled tasks such as reconnaissance, exploitation, data theft, propaganda production, surveillance workflows and research. Humans still selected the targets, set the goals and reviewed important outputs.
In other words, the people involved act more like managers than operators. They decide what to aim at and check the results, while software does the repetitive and time-consuming steps. This can let a small group do work that once needed a larger team.
Cybercrime
The report describes attackers using AI to industrialise several familiar activities:
- Credential theft↗
- Cloud compromise
- Phishing↗
- Vulnerability↗ research
- Extraction of sensitive data from downstream organisations, meaning the customers or partners of an initial victim
The techniques themselves are not new. The change is speed and scale.
Influence operations
Influence campaigns used persistent agent memory, fabricated news sites, fake journalists, synthetic personas and multilingual content produced at scale. The report notes, however, that engagement with this material remained limited. Producing large amounts of content is easier than persuading real people to pay attention to it.
Surveillance and repression
Cases in this category included automated dossiers on individuals, biometric analysis, targeting of people across borders, coercive recruitment, and systems that kept running locally after access to the AI service was revoked. That last point is a useful reminder that cutting off a service does not always undo what has already been built with it.
Biological and weapons research
The report says AI supported advanced scientific and military work. It generally does not establish completed biological weapons or operational battlefield deployment. This is worth keeping in mind: the concern is about assistance and capability, and the highlights do not claim that such weapons were produced.
Why it matters for everyone
You do not need to run a company or a security team to be affected. Faster, cheaper attack tools mean more convincing phishing messages, more automated scanning for weak accounts, and more synthetic content online. At the same time, the report shows that AI providers can detect and study misuse, which supports the case for transparency about it.
What you can do
- Assume messages can be polished. Good spelling and a natural tone no longer signal that an email or message is genuine. Verify unexpected requests through a separate, trusted channel.
- Use strong, unique passwords and passkeys or multi-factor authentication↗. Credential theft is a key target, so make stolen passwords less useful.
- Keep software and cloud settings up to date. Automated vulnerability research rewards anyone who leaves known flaws unpatched.
- Check sources. Be cautious of unfamiliar news sites and accounts, especially those that seem to appear suddenly and post in many languages.
- If you use AI agents yourself, give them only the access they need and keep a person in the loop for important actions.
The report's overall message is not that AI has made attacks unstoppable. It is that the tasks around an attack are becoming easier to automate, so basic security habits matter more, not less.
Source: Schneier on Security